In today’s fast-paced digital world, understanding and managing risks isn’t just a good idea, it’s absolutely essential. Whether you’re a bustling startup or a well-established enterprise, your valuable assets are constantly exposed to potential threats. But how do you go about identifying these risks, assessing their potential impact, and putting effective safeguards in place? It can feel like a monumental task, especially if you’re starting from scratch.
That’s where a structured approach comes into play. Instead of tackling risks haphazardly, an asset-based risk assessment helps you systematically identify what truly matters to your organization and then build your defense strategy around those critical elements. The good news is, you don’t have to reinvent the wheel. A well-designed asset based risk assessment template can provide the framework you need to simplify this complex process, ensuring you cover all your bases effectively.
Understanding the Core of Asset-Based Risk Assessment
Let’s talk about what an asset-based risk assessment really means. Imagine your organization as a treasure chest. Inside, you have all sorts of valuable items – not just money, but also important documents, unique technologies, the reputation you’ve worked so hard to build, and even the people who make everything run. An asset-based assessment starts by meticulously listing these “treasures” or assets. It’s about recognizing that not all assets are created equal; some are absolutely critical to your operations, while others, though important, might not bring your whole system crashing down if compromised.
Once you’ve identified your key assets, the next step is to consider what could possibly go wrong. We’re talking about threats – malicious software, natural disasters, human error, or even a disgruntled employee. For each threat, you then need to identify vulnerabilities, which are weaknesses in your current defenses that a threat could exploit. For example, an unpatched server (vulnerability) could be exploited by a ransomware attack (threat) to compromise your critical customer data (asset). This systematic approach helps paint a clear picture of potential dangers.
This is precisely where having a solid asset based risk assessment template becomes invaluable. It acts as your guided checklist, ensuring you don’t overlook any crucial steps or forget to consider certain types of assets or threats. Without a template, it’s easy to get lost in the details or prioritize risks based on gut feeling rather than objective analysis. The template provides a standardized way to document your assets, potential threats, and existing controls, making the entire process transparent and repeatable.
Ultimately, this structured approach allows you to make informed decisions about where to invest your security efforts. You’re not just throwing money at every potential problem; you’re strategically protecting your most vital assets against the most likely and impactful threats. Think of it as tailoring a suit for your security needs, rather than buying one off the rack that doesn’t quite fit.
Identifying Your Crown Jewels (Assets)
- **Information Assets:** Customer data, intellectual property, financial records, business strategies.
- **Software Assets:** Operating systems, applications, databases, proprietary code.
- **Hardware Assets:** Servers, workstations, network devices, mobile devices.
- **Physical Assets:** Buildings, data centers, office equipment.
- **Human Assets:** Key personnel, specialized skills, institutional knowledge.
- **Intangible Assets:** Brand reputation, customer trust, market share, legal rights.
Pinpointing Threats and Vulnerabilities
- **Threats:** Malware, phishing, denial of service attacks, natural disasters, human error, insider threats, hardware failure.
- **Vulnerabilities:** Unpatched software, weak passwords, lack of employee training, inadequate physical security, outdated security policies, single points of failure.
Building Your Own Practical Asset-Based Risk Assessment Template
While ready-made templates are a fantastic starting point, the real power lies in customizing an asset based risk assessment template to fit your unique organizational context. No two businesses are exactly alike, and neither are their risk profiles. Your template should reflect your specific industry, regulatory requirements, operational environment, and the particular assets you hold dear. Think of it as a living document, something that you’ll revisit and refine over time as your business evolves and new threats emerge.
When you’re designing or adapting your template, you’ll want to ensure it captures all the essential information needed to make sound risk management decisions. This includes not just listing assets and threats, but also systematically evaluating the likelihood of a threat exploiting a vulnerability and the potential impact if it does. This quantitative or qualitative assessment helps you prioritize risks, focusing your resources where they’ll have the greatest effect.
A good template will also encourage you to document existing controls and propose new mitigation strategies. What are you already doing to protect your assets? Are those measures effective? What else needs to be done to reduce the risk to an acceptable level? By breaking down these elements clearly within the template, you create an actionable plan rather than just a list of problems. It becomes a roadmap for improving your security posture.
Finally, remember that the goal isn’t just to fill out a form, but to foster a culture of continuous risk awareness and improvement. Your template should be user-friendly enough that different teams can contribute meaningfully, and comprehensive enough to provide valuable insights for leadership. Regularly reviewing your completed assessments and updating your template based on new learnings is crucial for maintaining an agile and effective risk management program.
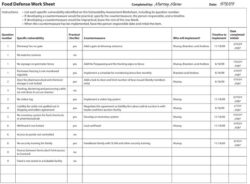
- **Asset ID & Description:** Unique identifier and detailed description of the asset.
- **Asset Owner:** The individual or department responsible for the asset.
- **Asset Classification:** How critical the asset is (e.g., High, Medium, Low).
- **Potential Threats:** Specific threats targeting this asset.
- **Existing Vulnerabilities:** Weaknesses that could be exploited.
- **Likelihood of Occurrence:** Probability of the threat exploiting the vulnerability (e.g., High, Medium, Low).
- **Potential Impact:** Consequences if the risk materializes (e.g., Financial, Reputational, Operational).
- **Calculated Risk Level:** A combination of likelihood and impact (e.g., Critical, High, Moderate, Low).
- **Current Controls:** Security measures already in place.
- **Recommended Mitigation Strategies:** Actions to reduce the risk.
- **Residual Risk:** The risk level after new controls are implemented.
- **Review Date & By Whom:** For ongoing maintenance and accountability.
Embracing an asset-based approach to risk assessment is a proactive step towards safeguarding your organization’s future. By systematically identifying your most valuable assets, understanding the threats they face, and evaluating the potential impact, you equip yourself with the knowledge to make informed decisions. This methodical process helps ensure that your resources are allocated efficiently, building robust defenses where they are needed most.
Taking the time to implement and regularly review such a framework isn’t just about compliance; it’s about resilience. It empowers you to navigate the complex landscape of modern risks with confidence, protecting your vital operations, reputation, and the trust of your stakeholders. Investing in a clear and actionable risk assessment strategy today will undoubtedly pay dividends in the security and stability of your organization tomorrow.