In today’s interconnected digital world, securing access to sensitive information and systems is paramount for any organization. Every day, countless transactions, communications, and operations rely heavily on robust electronic authentication methods, which act as the gatekeepers to our most valuable digital assets. From logging into your online banking to accessing corporate networks, the integrity and strength of these authentication processes directly impact overall security posture. Without proper safeguards, even the most sophisticated systems can be compromised if the entry points are weak.

This is precisely where the need for a systematic approach to identifying and mitigating risks becomes critical. Understanding potential vulnerabilities and threats associated with your e-authentication mechanisms isn’t just good practice; it’s an absolute necessity. Organizations are increasingly looking for structured tools to guide them through this complex process, and a well-designed e authentication risk assessment template serves as an invaluable starting point, providing a clear framework for evaluating and enhancing security.
Understanding the Criticality of E Authentication Risk Assessments
The digital landscape is constantly evolving, bringing with it a continuous wave of new threats and sophisticated attack vectors. Cybercriminals are always seeking the weakest link, and often, that link lies within authentication processes. If an attacker can bypass or compromise your e-authentication, they gain unauthorized access to data, systems, and potentially the entire organizational infrastructure. This can lead to severe consequences, including data breaches, financial losses, reputational damage, and regulatory penalties. Therefore, proactively identifying and addressing these risks is not merely a technical task but a strategic imperative that safeguards business continuity and trust.
Conducting a thorough risk assessment for e-authentication involves much more than just checking a few boxes; it requires a deep dive into how users authenticate, the technologies involved, and the potential ways these processes could be exploited. It demands a holistic view, considering everything from password policies and multifactor authentication (MFA) implementations to single sign on (SSO) configurations and biometric solutions. Without a structured methodology, organizations risk overlooking critical vulnerabilities that could be exploited by malicious actors, leaving them exposed to significant harm.
This is where a dedicated e authentication risk assessment template proves its worth. It provides a standardized framework that ensures no stone is left unturned. By following a consistent process, organizations can systematically evaluate their authentication ecosystem, identify specific threats, analyze potential impacts, and prioritize mitigation strategies. This structured approach helps transform what could be an overwhelming task into a manageable and actionable security exercise, ensuring that all relevant aspects are considered and documented.
Ultimately, the goal is not just to identify risks but to understand them well enough to implement effective controls that reduce the likelihood and impact of successful attacks. A comprehensive assessment allows for informed decision-making, enabling organizations to allocate resources wisely to areas of highest risk. It moves security from a reactive stance to a proactive one, building resilience against the ever-present dangers of the digital world.
Key Components of an Effective Template
- Asset Identification and Valuation Clearly define what assets are being protected by the authentication mechanism and their value to the organization.
- Threat Identification Identify potential malicious acts or events that could compromise authentication, such as phishing, brute force attacks, credential stuffing, or insider threats.
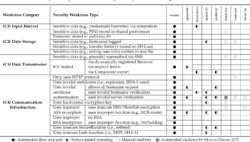
- Vulnerability Analysis Pinpoint weaknesses in the current authentication system, including weak password policies, lack of multifactor authentication, software bugs, or misconfigurations.
- Impact Assessment Evaluate the potential consequences of a successful attack, ranging from minor disruptions to severe data breaches or system downtime.
- Existing Controls Review Current security measures in place to mitigate identified threats and vulnerabilities.
- Risk Ranking and Prioritization Assign a risk level (e.g., high, medium, low) to each identified risk based on its likelihood and impact, allowing for focused remediation efforts.
- Control Recommendations Propose new or enhanced security controls to address the identified risks effectively.
- Residual Risk Assessment Determine the level of risk that remains after implementing new controls, ensuring ongoing monitoring.
Implementing Your E Authentication Risk Assessment Template for Maximum Security
Once you have an e authentication risk assessment template in hand, the real work begins: implementation. This isn’t a one-time task but rather an ongoing process that requires commitment and cross-functional collaboration. The first step involves gathering the right team. This usually includes IT security specialists, system administrators, compliance officers, and even representatives from business units whose applications or data rely heavily on the authentication processes being assessed. Their combined knowledge ensures a comprehensive view of the authentication landscape, covering both technical details and business implications.
Next, you’ll delve into the actual assessment using your chosen template as a guide. This involves systematically working through each section of the template, documenting your organization’s specific assets, identifying all relevant e-authentication methods in use, and meticulously cataloging potential threats and vulnerabilities. It’s crucial to be thorough and honest in this phase; an incomplete or biased assessment will lead to an inaccurate understanding of your risk posture. This often involves reviewing architecture diagrams, security policies, logs, and conducting interviews with personnel involved in managing and using authentication systems.
Following the identification phase, the template will guide you through assessing the likelihood and impact of each identified risk. This quantitative or qualitative analysis helps in prioritizing risks, allowing your team to focus remediation efforts where they will have the greatest effect. For instance, a risk with a high likelihood of occurring and a severe impact should obviously take precedence over a low-likelihood, low-impact risk. The template provides a structured way to assign these ratings and ensures consistency across different assessments.
Finally, the implementation phase culminates in developing and enacting a remediation plan. Based on the prioritized risks, specific controls and actions are recommended to mitigate them. This could involve strengthening password policies, deploying multifactor authentication across more systems, patching vulnerable software, or implementing continuous monitoring solutions. After controls are put in place, the template also helps in assessing the residual risk, ensuring that even after mitigation, any remaining risks are understood and accepted, or further addressed. This iterative process of assess, mitigate, and re-assess ensures your security posture continuously improves.
The ongoing nature of risk management means that your e authentication risk assessment template should not be filled out once and then forgotten. Regular reviews are essential, especially as your organization’s technology stack evolves, new threats emerge, or regulatory requirements change. Treat the template as a living document, a cornerstone of your security strategy that is revisited and updated periodically, or whenever significant changes occur within your authentication infrastructure. This dedication to continuous assessment and improvement is what truly builds and maintains a resilient digital environment.
Securing your digital environment is an ongoing journey, not a destination. By systematically identifying and addressing vulnerabilities in your authentication processes, organizations can significantly reduce their exposure to cyber threats and safeguard their critical assets. Embracing a structured approach to risk management empowers you to make informed decisions and allocate resources effectively, building a stronger defense against an ever-evolving threat landscape.
Proactive security measures are the bedrock of digital trust. Through diligent assessment and continuous improvement of your e-authentication mechanisms, you ensure that access to your systems remains robust, resilient, and ready to withstand the challenges of tomorrow. This commitment not only protects your organization but also instills confidence in your users and stakeholders.