In today’s fast-paced digital world, mobile banking has transformed how we manage our finances, offering unparalleled convenience and accessibility. From checking balances to transferring funds and paying bills, a vast array of financial services is now available right in the palm of our hand. However, this convenience also introduces a complex landscape of potential risks that financial institutions and users alike must navigate with extreme caution. Ensuring the security and integrity of these mobile platforms is not just good practice; it’s absolutely essential for maintaining trust and protecting sensitive data.

Understanding these inherent vulnerabilities and proactively addressing them is paramount for any financial service provider. A robust framework is needed to systematically identify, analyze, and mitigate potential threats before they can cause significant harm. This is precisely where a well-designed mobile banking risk assessment template becomes an invaluable tool, providing a structured approach to safeguard your digital banking ecosystem and build enduring customer confidence.
Why a Robust Mobile Banking Risk Assessment is Crucial
The digital frontier of mobile banking is constantly evolving, bringing with it an equally dynamic array of threats. Cybercriminals are always looking for new vulnerabilities to exploit, ranging from sophisticated malware designed to intercept credentials to phishing scams that trick users into revealing sensitive information. Unsecured Wi-Fi networks, outdated operating systems on user devices, and even vulnerabilities within the banking application itself can create openings for malicious actors. Without a clear and comprehensive assessment, these potential weaknesses can remain undetected, leaving institutions and their customers exposed to significant financial and reputational damage.
Beyond the direct threat of cyberattacks, financial institutions face stringent regulatory requirements. Compliance with data protection laws like GDPR, CCPA, and various anti-money laundering (AML) regulations is not optional. A lapse in security can lead to hefty fines, legal battles, and a severe loss of customer trust, which can be incredibly difficult to rebuild. A thorough risk assessment is not just about preventing breaches; it’s about demonstrating due diligence and a commitment to protecting customer assets and privacy, fulfilling regulatory obligations, and safeguarding the institution’s long-term viability.
Key Components of an Effective Mobile Banking Risk Assessment
A truly effective assessment dives deep into every layer of the mobile banking environment, from the back-end infrastructure to the end-user device. It considers various vectors of attack and potential points of failure, ensuring no stone is left unturned in the pursuit of a secure platform. This holistic view helps to build a resilient system that can withstand the ever-growing pressures of the digital threat landscape.
- Technology and Infrastructure Risks: This includes scrutinizing the security of the mobile banking application itself, the underlying server infrastructure, data encryption methods, API security, and protection against common web vulnerabilities such as SQL injection or cross-site scripting.
- User Behavior Risks: This category examines the human element, including the risk of users falling victim to phishing or social engineering attacks, using weak passwords, or accessing banking services on compromised or public devices. User education and secure authentication mechanisms are key mitigations here.
- Operational Risks: This covers internal processes, third-party vendor risks (e.g., payment processors, cloud providers), incident response plans, fraud detection systems, and the adequacy of internal controls to prevent unauthorized access or manipulation of data.
- Regulatory and Compliance Risks: Ensuring adherence to all relevant financial regulations, data privacy laws, and industry standards is critical. This involves verifying that the mobile banking platform incorporates necessary controls for KYC (Know Your Customer) and AML requirements.
By systematically evaluating each of these components, institutions can gain a clear picture of their risk posture, prioritize vulnerabilities, and allocate resources effectively to implement robust security measures.
Building and Implementing Your Mobile Banking Risk Assessment Template
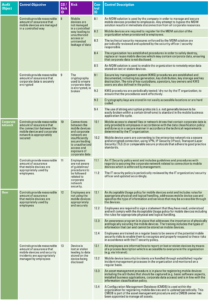
Creating and deploying a comprehensive mobile banking risk assessment template is a strategic undertaking that requires careful planning and a thorough understanding of your specific operational environment. It’s not about finding a one-size-fits-all solution, but rather customizing a framework that accurately reflects your unique services, customer base, and threat landscape. The process typically begins by defining the scope of the assessment, identifying all assets involved, and then systematically evaluating potential threats and vulnerabilities associated with each asset.
A practical approach involves several key steps. First, identify critical assets within your mobile banking ecosystem, which might include customer data, transaction systems, intellectual property, and even the reputation of your brand. Next, enumerate potential threats, such as malware, data breaches, denial-of-service attacks, and insider threats. Following this, identify vulnerabilities that could allow these threats to materialize, like unpatched software, weak authentication protocols, or inadequate employee training. Once these are identified, assess the likelihood of each threat occurring and the potential impact if it does, allowing you to prioritize risks based on their severity.
Once risks are identified and prioritized, the next crucial phase involves developing and implementing mitigation strategies and controls. These could range from technical safeguards like multi-factor authentication (MFA), robust data encryption, and regular penetration testing, to operational controls such as stringent employee training, comprehensive incident response plans, and continuous fraud monitoring. User education campaigns are also vital to empower customers to recognize and avoid common scams, adding another layer of defense against socially engineered attacks. Investing in these measures is a proactive step toward fortifying your defenses.
It’s important to remember that a mobile banking risk assessment template is not a static document. The digital threat landscape is constantly evolving, with new vulnerabilities and attack methods emerging regularly. Therefore, the assessment process must be continuous and dynamic. Regular reviews, updates, and re-assessments are essential to ensure that your security posture remains robust against emerging threats. This ongoing commitment to security allows financial institutions to adapt quickly, maintaining a strong defense against the ever-present challenges of the cyber world.
Adopting a structured approach to risk management in mobile banking is no longer a luxury but a fundamental necessity. By systematically identifying, assessing, and mitigating potential risks, financial institutions can not only protect their invaluable assets and their customers’ sensitive information but also uphold their reputation and ensure compliance with regulatory standards. It’s about building a resilient and trustworthy digital environment where convenience and security coexist seamlessly.
Prioritizing security through diligent risk assessment empowers institutions to confidently navigate the complexities of the digital age, fostering a secure and reliable mobile banking experience for everyone. This proactive stance ensures that as technology advances, the safety and integrity of financial transactions remain at the forefront, safeguarding the future of banking in an increasingly connected world.