In today’s fast-evolving digital landscape, managing vast amounts of information isn’t just about storage; it’s about intelligent governance. Organizations globally grapple with the challenge of balancing data utility with robust protection, all while navigating an increasingly complex web of regulations. From personal data privacy to intellectual property, the stakes for mishandling information have never been higher, impacting not only legal standing but also reputation and financial health.

Understanding where your vulnerabilities lie and what potential threats your information assets face is the cornerstone of effective data management. This is precisely where a structured approach becomes indispensable. Employing an information governance risk assessment template provides a clear, systematic framework to identify, analyze, and mitigate risks associated with your organization’s information, ensuring compliance and fostering a culture of responsible data stewardship.
Why a Robust Information Governance Risk Assessment is Non-Negotiable
The digital age brings with it an unprecedented volume of data, and with that, an equally unprecedented number of risks. Organizations are under constant pressure from various fronts: sophisticated cyber threats seeking to exploit vulnerabilities, an ever-expanding patchwork of global and regional privacy regulations like GDPR and CCPA, and the internal challenges of managing information across diverse systems and departments. Without a clear understanding of these risks, an organization operates blindly, leaving itself exposed to potentially catastrophic consequences.
Ignoring information governance risks is akin to leaving the front door unlocked in a bustling city. The repercussions can range from hefty regulatory fines that significantly impact the bottom line to severe reputational damage that erodes customer trust and market standing. Beyond financial and public perception, data breaches can lead to operational disruptions, loss of critical business intelligence, and even legal action from affected parties. Proactively identifying these risks, therefore, isn’t just good practice; it’s essential for business continuity and resilience.
A well-executed information governance risk assessment shifts an organization from a reactive stance to a proactive one. Instead of waiting for an incident to occur, it allows you to anticipate potential problems, evaluate their likelihood and impact, and implement preventative measures. This forward-thinking approach not only reduces the probability of adverse events but also minimizes their severity should they occur. It empowers decision-makers with the insights needed to allocate resources effectively, focusing on the areas of greatest risk.
Key Areas a Template Helps You Evaluate
- Data privacy compliance with regulations like GDPR, CCPA, and HIPAA.
- Identification of data security vulnerabilities across systems and networks.
- Assessment of data retention and disposition policies, ensuring legal and business needs are met.
- Evaluation of information accessibility, integrity, and availability for operational continuity.
- Analysis of third-party vendor risks and their impact on your information governance posture.
- Review of employee awareness and training programs regarding information handling.
Utilizing a comprehensive information governance risk assessment template ensures that no critical area is overlooked. It standardizes the assessment process, allowing for consistent evaluations over time and across different departments. This structured methodology helps pinpoint weaknesses, prioritize remediation efforts, and build a stronger, more compliant information environment that can withstand the pressures of the modern data landscape.
Building Your Effective Information Governance Risk Assessment Template
Developing an effective information governance risk assessment template doesn’t have to be an overwhelming task. It begins with a clear understanding of your organization’s unique information ecosystem and a commitment to detail. The template serves as a dynamic tool, one that evolves with your business and the threat landscape. Start by clearly defining the scope of your assessment; what information assets are you examining, and what are the boundaries of this particular review? This initial step is crucial for ensuring the assessment is focused and manageable.
Once the scope is established, the next phase involves identifying your critical information assets. This isn’t just about servers and databases; it includes sensitive documents, intellectual property, customer data, employee records, and even informal communications. For each asset, you need to articulate its value, its location, who has access to it, and how it is currently protected. Simultaneously, brainstorm and document potential threats – these could be anything from cyberattacks and insider threats to natural disasters or system failures. Paired with threats, identify vulnerabilities – the weaknesses in your systems, processes, or controls that could be exploited.
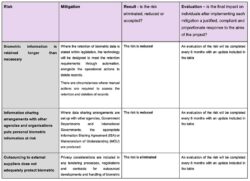
After identifying assets, threats, and vulnerabilities, the template guides you in analyzing the likelihood of a threat exploiting a vulnerability and the potential impact if it does. This analysis often involves qualitative and quantitative measures, assigning risk levels (e.g., low, medium, high) based on predetermined criteria. For instance, a high likelihood of a data breach combined with a severe impact on customer trust and regulatory fines would result in a high-priority risk requiring immediate attention. This systematic evaluation helps in differentiating between minor concerns and significant exposures.
The final, and arguably most crucial, step in utilizing an information governance risk assessment template is the development of mitigation strategies and controls. For each identified high-priority risk, specific actions must be outlined to reduce its likelihood or impact. These could include implementing new security technologies, updating policies, providing employee training, or enhancing data backup procedures. The template should also include a section for assigning ownership of these actions, setting deadlines, and tracking progress. Regular review and updates of the template and the risks it addresses are vital, as the information environment is constantly changing.
An effective template encourages continuous improvement, transforming risk assessment from a one-off event into an integral part of your organization’s operational rhythm. By systematically applying the steps within your tailored information governance risk assessment template, you not only address current risks but also build a resilient framework capable of adapting to future challenges and opportunities in the digital realm.
Embracing a proactive approach to information governance through a structured risk assessment is an investment that yields significant returns. It fortifies your organization against an array of potential threats, ensuring the integrity, security, and compliance of your most valuable information assets. By systematically identifying and addressing vulnerabilities, you not only protect against financial penalties and reputational damage but also cultivate a robust foundation for trust and operational excellence.
Ultimately, a well-defined and regularly utilized framework empowers your organization to navigate the complexities of data management with confidence. It allows you to transform potential liabilities into managed risks, fostering an environment where information serves as an enabler for growth and innovation, rather than a source of constant concern. This strategic foresight ensures long-term stability and success in an increasingly data-dependent world.