Navigating the intricate landscape of modern finance means constantly facing a barrage of evolving digital threats. For banks, safeguarding sensitive customer data and maintaining the integrity of financial systems is not just a regulatory requirement; it is the very cornerstone of trust and operational continuity. A single cybersecurity incident can erode years of reputation and incur significant financial penalties, making proactive risk management an absolute necessity in today is interconnected world.
This is precisely why having a robust framework for identifying, assessing, and mitigating information technology risks is non negotiable. A well structured approach provides clarity and consistency, ensuring that no potential weak point is overlooked. It helps institutions systematically evaluate their digital vulnerabilities and prioritize actions that protect their assets most effectively. Without such a framework, banks would be left guessing, reactive instead of proactive, and significantly more susceptible to the ever increasing sophistication of cyberattacks.
Why Your Bank Needs a Robust IT Risk Assessment Template
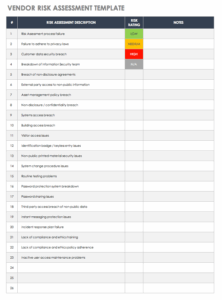
In the complex and highly regulated banking sector, an effective IT risk assessment template for banks is far more than a simple checklist; it is a strategic tool vital for survival and growth. Financial institutions operate under intense scrutiny from regulators worldwide, all of whom demand demonstrable evidence of sound risk management practices. From Basel III requirements focusing on operational risk to stringent data protection mandates like GDPR and the upcoming Digital Operational Resilience Act DORA in Europe, failing to meet these standards can lead to severe fines, legal action, and a dramatic loss of public confidence.
Consider the consequences of a major data breach or a system outage. Beyond the immediate financial losses from fraud or operational disruption, there is the long term damage to reputation. Customers entrust banks with their most valuable assets and personal information; any perceived weakness in security can send them seeking services elsewhere. A comprehensive template ensures that all potential IT related risks are systematically identified and evaluated, from network vulnerabilities and software flaws to human error and third party vendor risks, providing a clear picture of an institution is security posture.
A standardized template brings numerous benefits to the table. It promotes consistency across different departments and risk assessment teams, ensuring that all risks are evaluated using the same criteria and methodologies. This standardization vastly improves the comparability of risk profiles over time and across various business units. It streamlines the assessment process itself, reducing the time and resources required to conduct thorough evaluations, which is a significant advantage in fast paced environments.
Ultimately, a tailored IT risk assessment template for banks empowers leadership with the insights needed to make informed decisions about risk acceptance, mitigation strategies, and resource allocation. It moves the conversation from abstract concerns to concrete action plans, enabling banks to proactively address threats before they materialize into costly incidents. This structured approach helps in building a resilient digital infrastructure capable of withstanding the dynamic challenges of the financial cyber threat landscape.
Key Components of an Effective Template
An effective IT risk assessment template is built upon several foundational elements that collectively provide a holistic view of an institution is risk environment. These components ensure that every aspect of information technology risk is thoroughly examined and documented.
* Asset Identification
* Threat Identification
* Vulnerability Analysis
* Control Assessment
* Risk Likelihood and Impact
* Risk Prioritization
* Mitigation Strategies
* Reporting and Monitoring
Implementing and Maintaining Your IT Risk Assessment Template
Successfully implementing an IT risk assessment template requires a thoughtful approach that goes beyond merely filling out forms. It begins with securing strong leadership buy in and clearly communicating the purpose and benefits of the template to all stakeholders across the organization. Engaging key personnel from IT, security, compliance, and various business units is crucial for gathering accurate data and ensuring that the template addresses the specific risks pertinent to different operational areas. It is a collaborative effort that fosters a shared understanding of risk responsibility.
Once the template is introduced, a phased implementation can be highly effective. Starting with a pilot program in a specific department or system allows for fine tuning the template and the assessment process, identifying any unforeseen challenges, and making necessary adjustments before a wider rollout. This iterative process helps build confidence in the tool and minimizes disruption, making the transition smoother for all involved. Providing adequate training to those who will be using the template is also paramount to ensure consistent application and accurate risk reporting.
The landscape of IT risks is not static; it is constantly evolving with new technologies, emerging threats, and changes in regulatory requirements. Therefore, the IT risk assessment template itself must be treated as a living document, subject to regular review and updates. Periodic reassessments, perhaps annually or whenever significant changes to the IT environment occur, are essential to maintain its relevance and effectiveness. This ongoing process helps banks stay ahead of potential threats and ensures that their risk management strategies remain robust and aligned with current realities.
Furthermore, integrating the insights gained from the template into broader enterprise risk management frameworks and incident response plans enhances an institution is overall resilience. The data collected through the risk assessment can inform strategic decisions, guide resource allocation for security investments, and refine emergency procedures. This holistic approach ensures that IT risk management is not an isolated function but an integral part of the bank is comprehensive strategy for safeguarding its operations and reputation in a digitally driven world.
Adopting a systematic approach to IT risk assessment is a fundamental pillar for any financial institution aiming for long term stability and sustained trust in the digital age. It moves banks from a reactive stance to a proactive one, allowing them to anticipate and neutralize threats before they can inflict damage. The commitment to consistently apply, update, and integrate a robust risk assessment framework into daily operations ultimately strengthens the entire organization against the relentless tide of cyber challenges.