In today’s fast-paced digital world, your business’s IT infrastructure is the backbone of its operations. From managing customer data to facilitating daily tasks, everything relies on a robust and secure technological foundation. But with great power comes great responsibility, and the digital landscape is fraught with potential threats that could disrupt your services, compromise sensitive information, or even halt your business entirely. Understanding these risks isn’t just a good idea; it’s a critical component of modern business strategy.
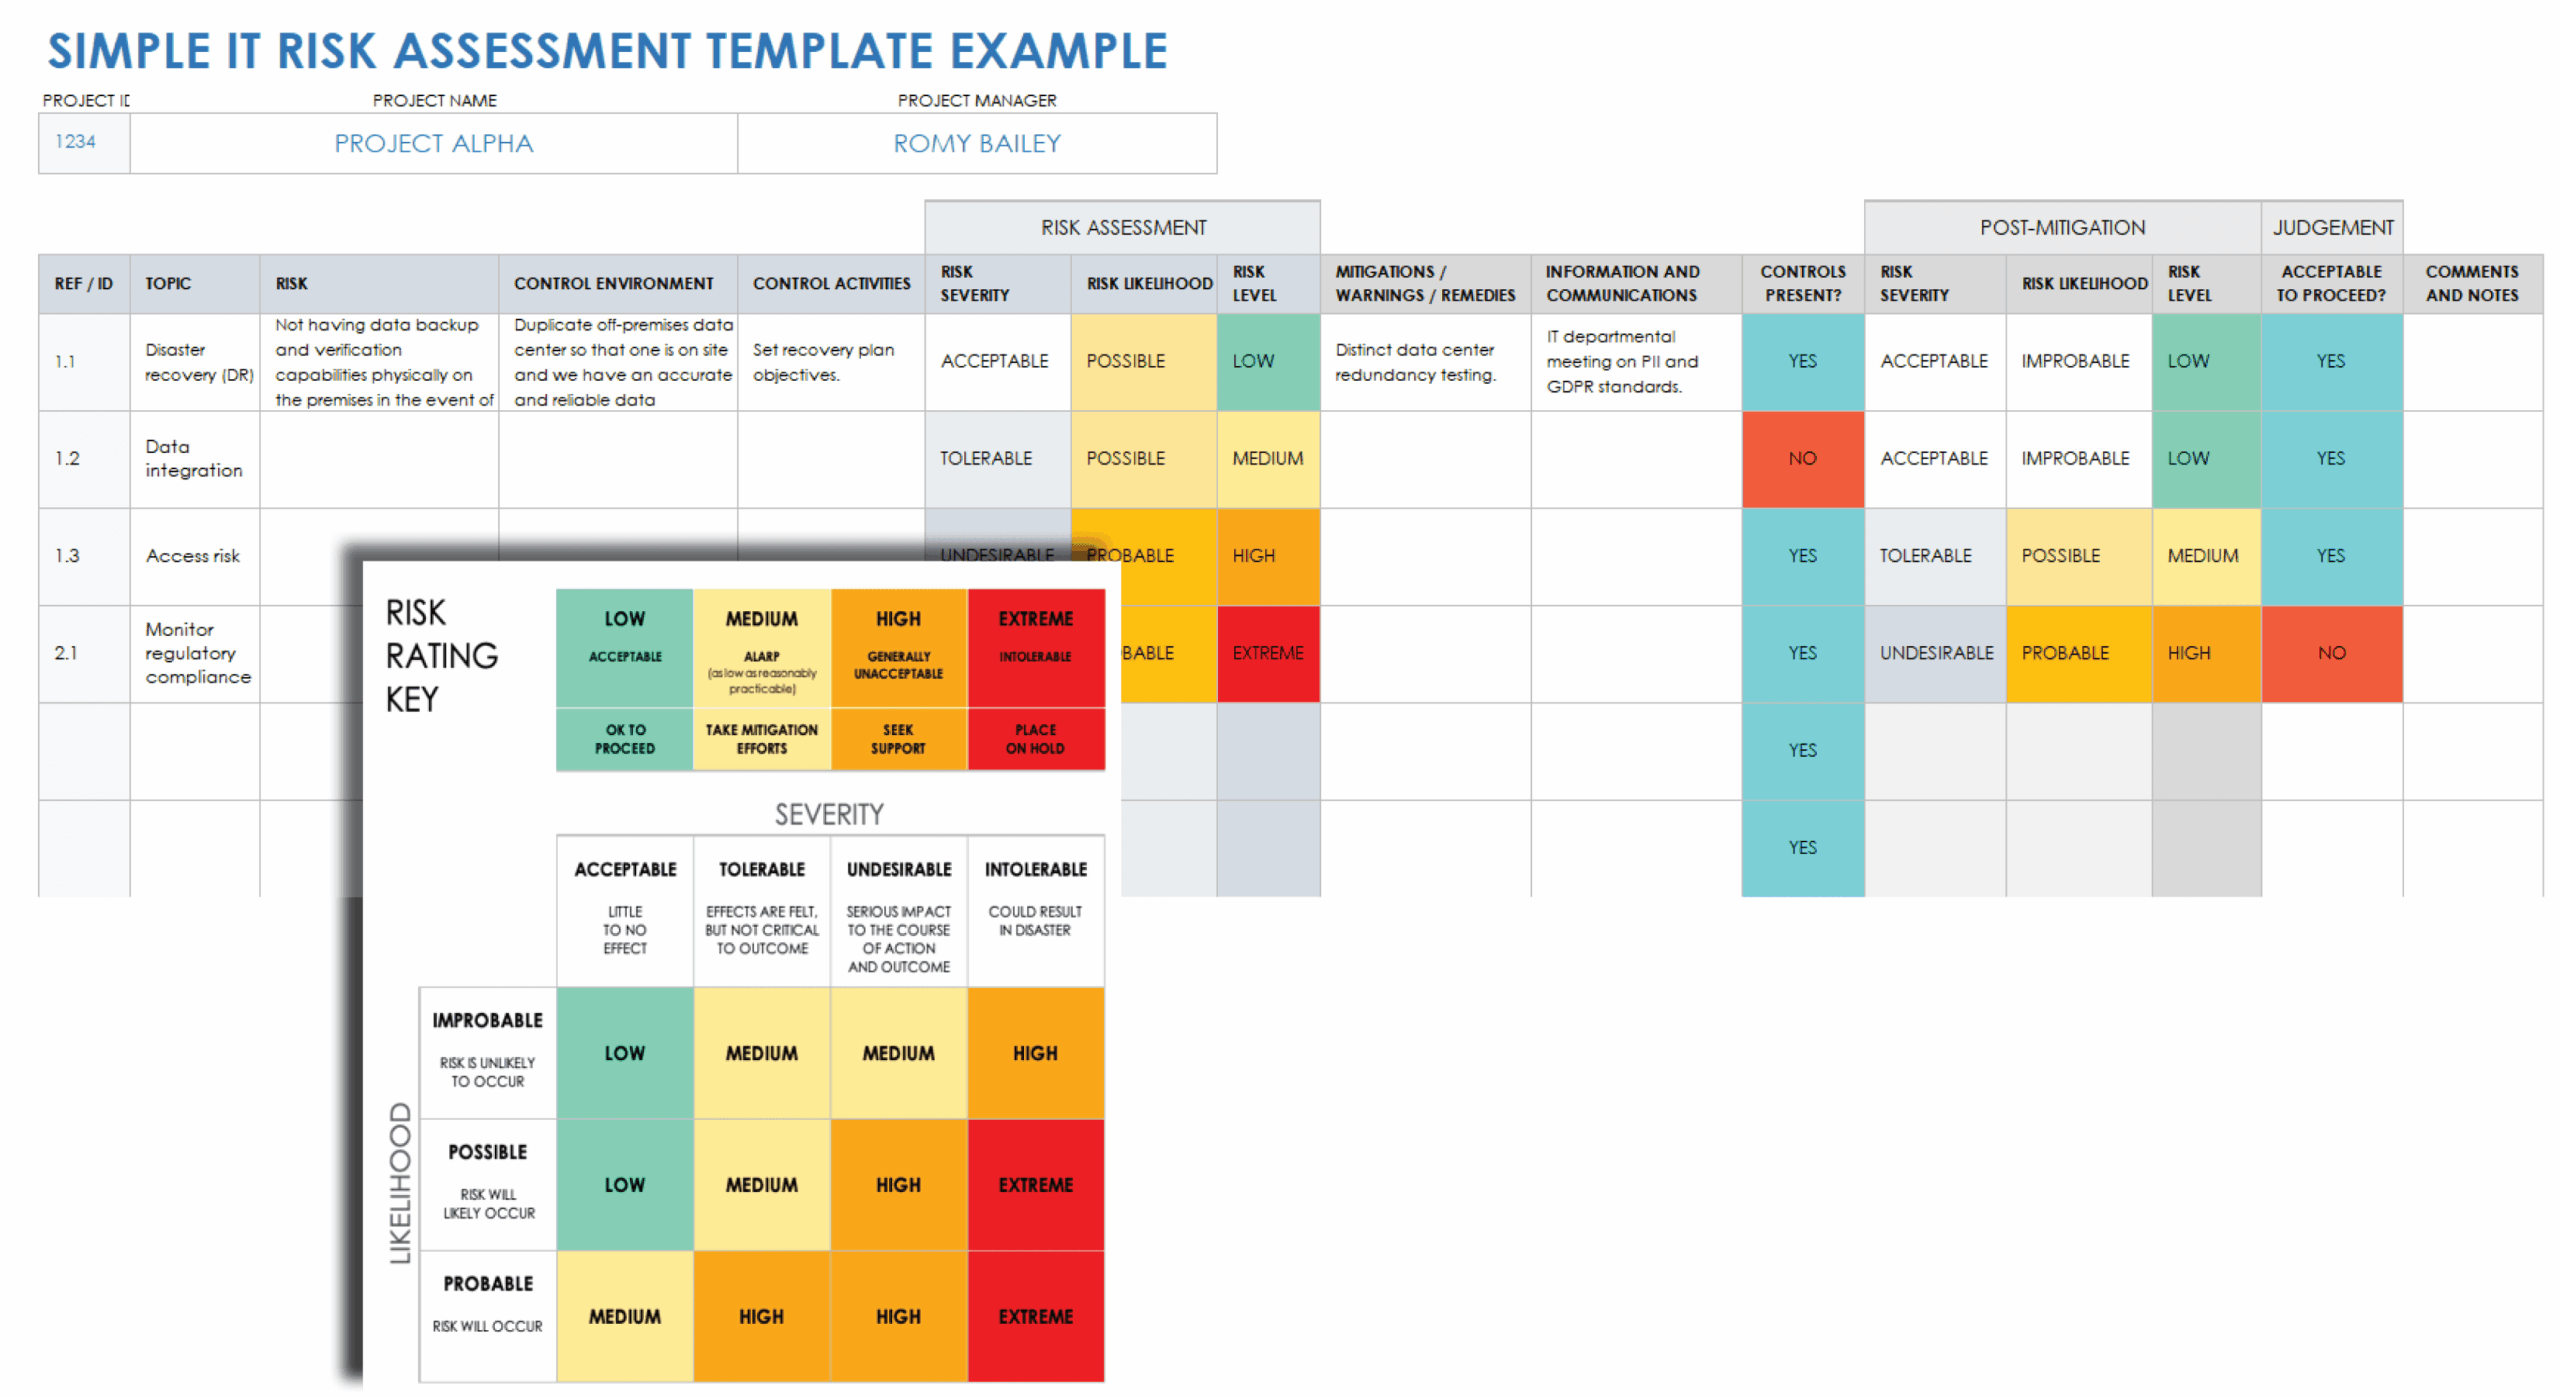
This is precisely where an effective risk assessment comes into play. It’s about proactively identifying, evaluating, and mitigating potential vulnerabilities before they turn into costly incidents. While the idea of conducting a thorough IT risk assessment might seem daunting, especially for businesses with complex systems, having a well-structured it infrastructure risk assessment template can dramatically simplify the process, making it manageable and highly effective.
Understanding the Core Components of an IT Infrastructure Risk Assessment
Embarking on an IT risk assessment can feel like navigating a maze without a map. That’s why a clear, comprehensive approach is essential. A robust assessment goes beyond just identifying a few weak spots; it’s a systematic examination of your entire IT ecosystem to pinpoint what could go wrong, how likely it is to happen, and what the impact would be. It helps you make informed decisions about where to invest your security resources for maximum protection and efficiency.
Imagine trying to secure your house without knowing where the doors and windows are, or what valuable items you possess. You wouldn’t know where to put locks or alarms! Similarly, an IT infrastructure risk assessment template guides you through understanding your digital assets, recognizing potential threats, and evaluating your existing safeguards. It provides a structured framework that ensures no critical area is overlooked, helping you build a stronger, more resilient IT environment.
The real power of a template lies in its ability to standardize your assessment process. This consistency means you can conduct repeat assessments over time, comparing results and demonstrating tangible improvements in your security posture. It’s not just a one-time checkup; it’s an ongoing commitment to cybersecurity hygiene that protects your business from evolving threats.
Key Phases of a Comprehensive Risk Assessment
To make sure your assessment covers all bases, here are the fundamental stages you’ll typically move through:
- Asset Identification: What exactly are you trying to protect? This includes hardware, software, data, networks, and even the people who access them. You can’t protect what you don’t know you have.
- Threat Identification: What potential dangers could affect your assets? Think about malware, phishing attacks, insider threats, natural disasters, or hardware failures.
- Vulnerability Identification: What weaknesses in your current systems or processes could these threats exploit? This could be unpatched software, weak passwords, or lack of employee training.
- Risk Analysis: This is where you combine the likelihood of a threat exploiting a vulnerability with the potential impact it would have. This helps you prioritize which risks need immediate attention.
- Risk Treatment: Once risks are identified and analyzed, you decide how to manage them. This could involve mitigating the risk (implementing controls), accepting it (if the cost of mitigation outweighs the impact), avoiding it (changing operations), or transferring it (insurance).
- Monitoring and Review: Risks aren’t static. You need to regularly review your risk assessment, update it with new information, and monitor the effectiveness of your controls.
Practical Steps to Implement Your IT Infrastructure Risk Assessment Template
Once you have your chosen it infrastructure risk assessment template, the next step is putting it into action. This isn’t just about filling in boxes; it’s an investigative process that requires collaboration and keen observation. Start by clearly defining the scope of your assessment. Are you evaluating your entire infrastructure, or focusing on a specific system or department? A well-defined scope prevents you from getting overwhelmed and ensures your efforts are concentrated where they’re most needed.
Gathering information is crucial. This means engaging with various teams across your organization. Talk to your IT specialists about network configurations and software versions, interview department heads about critical data and applications, and even consult with human resources regarding employee access policies. The more data you collect, the more accurate and useful your risk assessment will be. Don’t be afraid to ask tough questions and dig deep into current practices.
After populating your template with identified assets, threats, and vulnerabilities, the real analysis begins. This is where you leverage the template’s structure to systematically assign likelihood and impact scores to each risk. This process helps you visualize and prioritize risks, often leading to a clearer understanding of your most critical security gaps. Remember, not all risks are created equal, and your template helps you differentiate between a minor inconvenience and a potential catastrophe.
Finally, the insights gained from your assessment should drive actionable plans. The template isn’t just an exercise; it’s a roadmap for improving your security posture. Develop mitigation strategies for high-priority risks, assign owners for each action, and set clear timelines for implementation. A living document, your risk assessment template should be regularly revisited and updated, ensuring that your IT infrastructure remains protected against the ever-evolving landscape of digital threats.
Effectively utilizing an it infrastructure risk assessment template transforms a complex, abstract challenge into a structured, manageable process. It empowers your business to not only react to security incidents but to proactively prevent them, ensuring operational continuity and protecting your valuable digital assets. By making risk assessment a regular part of your business strategy, you build a more secure, resilient, and trustworthy enterprise for the long haul.