In today’s interconnected digital world, having an online presence, whether it is a simple blog or a complex e-commerce platform, comes with inherent risks. Cyber threats are constantly evolving, ranging from sophisticated data breaches to malicious software attacks, and the consequences of a security incident can be severe, impacting your reputation, financial stability, and customer trust. Proactively addressing these vulnerabilities is no longer optional; it is an absolute necessity for anyone managing a website.
This is precisely where a structured approach to identifying and mitigating potential dangers becomes invaluable. Instead of waiting for an incident to occur, a thorough security risk assessment allows you to pinpoint weaknesses before they can be exploited. And to make this crucial process manageable and consistent, having a reliable framework in place, often in the form of a dedicated template, is incredibly helpful.
Understanding Why a Site Security Risk Assessment Template is Crucial
Imagine navigating a minefield without a map. That is essentially what managing a website without understanding its security risks feels like. Digital assets, including your website’s data, user information, and operational functionality, are precious. A single successful attack can lead to data loss, service downtime, legal repercussions, and a significant blow to your brand’s credibility. Knowing where your site is vulnerable and what potential threats lurk is the first step toward building robust defenses.
A well-designed site security risk assessment template provides a systematic way to identify, evaluate, and prioritize these potential dangers. It acts as a comprehensive checklist and a guiding document, ensuring that no critical area is overlooked. This structured approach helps organizations move beyond guesswork, allowing them to make informed decisions about where to invest their security resources most effectively. It transforms a daunting, abstract concept into a series of manageable steps, providing clarity and direction.
Furthermore, adhering to a standardized assessment process is often a requirement for various compliance regulations, such as GDPR, CCPA, or HIPAA, depending on the type of data your site handles. Demonstrating that you have a formal process for identifying and addressing security risks can be vital in avoiding hefty fines and maintaining legal standing. Beyond compliance, it simply provides peace of mind, knowing that you have proactively identified and addressed potential weaknesses before a malicious actor does. Utilizing a detailed site security risk assessment template ensures you cover all the bases, from server configurations to application code.
Key Phases of a Security Risk Assessment
The journey of understanding your site’s security posture typically involves several distinct yet interconnected phases. Each step builds upon the last, contributing to a holistic view of your risk landscape.
- Identify Assets: Begin by listing everything of value within your site’s ecosystem. This includes servers, databases, applications, intellectual property, customer data, and even the reputation of your brand.
- Identify Threats: Next, consider all possible events that could cause harm to your identified assets. This might include malware, phishing attacks, denial of service attacks, insider threats, natural disasters, or even human error.
- Identify Vulnerabilities: Pinpoint the weaknesses in your current systems or processes that could be exploited by the identified threats. This could be outdated software, weak passwords, misconfigured firewalls, or lack of employee training.
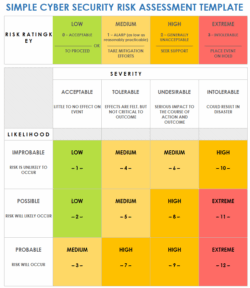
- Analyze Risks: Combine the identified threats and vulnerabilities to determine the likelihood of an exploit occurring and the potential impact if it does. This phase often involves qualitative or quantitative scoring.
- Determine Impact: Assess the potential consequences of a security incident, both financially and reputationally. Consider direct costs, lost revenue, legal fees, and damage to customer trust.
- Recommend Controls: Finally, propose specific security measures and strategies to mitigate the identified risks. These controls could be technical, such as implementing firewalls, or administrative, like developing new security policies.
Building Your Own Effective Site Security Risk Assessment Template
Once you understand the fundamental importance of assessing your site’s security, the next natural step is to consider how you can effectively implement this process. While many generic templates exist online, the most effective approach often involves customizing or building a template that perfectly aligns with your specific operational context, technology stack, and business objectives. Your site is unique, and so too should be the detailed analysis of its potential weaknesses.
Start by clearly defining the scope of your assessment. Are you evaluating your entire web infrastructure, a specific application, or just a particular set of data? A clear scope prevents scope creep and ensures your efforts are focused. Next, detail all the components that make up your site. This includes hosting environments, content management systems, plugins, custom code, third-party integrations, and even the administrative processes involved in managing your content and users. Each of these components represents a potential entry point for threats.
After listing your assets, brainstorm potential threats from various angles. Think like an attacker. What motivations might they have? What common attack vectors are prevalent for your type of site or industry? Consider external threats like hackers and malware, but also internal threats such as accidental data exposure by an employee. Documenting these threats systematically within your template helps ensure a comprehensive review, rather than relying solely on memory or current events.
Finally, a truly valuable template will guide you through the process of evaluating the likelihood of each risk occurring and the potential impact should it materialize. This assessment helps you prioritize your mitigation efforts. Not all risks are created equal, and your resources are finite. Focus on high-likelihood, high-impact risks first. Then, define clear mitigation strategies for each identified risk, assigning responsibilities and setting timelines for implementation. Regular review and updates to your template are crucial to keep pace with evolving threats and changes in your site’s architecture.
- Define Scope: Clearly outline what parts of your site and infrastructure are included in the assessment.
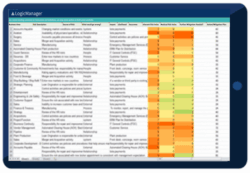
- List All Assets: Document every component and data type that constitutes your website.
- Brainstorm Potential Threats: Enumerate all possible malicious or accidental events that could harm your assets.
- Document Existing Controls: Note down any current security measures already in place to protect against threats.
- Assess Likelihood and Impact: For each risk, estimate how probable it is and how severe the consequences would be.
- Prioritize Risks: Rank risks based on their combined likelihood and impact scores to guide resource allocation.
- Formulate Mitigation Strategies: Develop actionable plans to reduce or eliminate identified risks.
- Regular Review: Schedule periodic reassessments to keep your security posture current and robust.
Securing your online presence is an ongoing journey, not a destination. The digital landscape is dynamic, with new threats and vulnerabilities emerging constantly. Embracing a proactive, structured approach to security risk assessment is therefore not a one-time task but a continuous cycle of evaluation, improvement, and adaptation.
By systematically identifying potential weaknesses and implementing robust controls, you are not just protecting your data and users; you are also safeguarding your reputation and ensuring the long-term stability and trustworthiness of your online operations. A well-executed assessment empowers you to build a more resilient and secure digital foundation, allowing you to focus on growth and innovation with confidence.