Navigating the complexities of modern business requires more than just a good product or service; it demands a robust understanding and management of the risks that could derail your operations. Every organization, regardless of size or industry, faces a unique set of challenges from financial fraud to data breaches, and even simple operational inefficiencies. The key to staying ahead and ensuring sustained success lies in proactively identifying these potential pitfalls and putting safeguards in place.

This is where a well-structured approach to internal control and risk assessment becomes indispensable. Instead of reacting to problems as they arise, imagine having a clear, systematic way to anticipate them, analyze their potential impact, and implement preventative measures. Such an approach not only protects your assets but also builds trust with stakeholders and fosters a culture of accountability within your team. A powerful tool for achieving this is a dedicated internal control risk assessment template.
Why Your Business Needs a Robust Internal Control Risk Assessment Template
Think about it this way: you wouldn’t embark on a long road trip without checking your car’s tires and oil, would you? Similarly, running a business without regularly assessing its vulnerabilities is akin to driving blindfolded. A robust internal control risk assessment template provides that much-needed visibility, acting as your dashboard for identifying, evaluating, and mitigating risks before they escalate into significant issues. It transforms an often daunting and abstract task into a manageable, step-by-step process.
This type of template is more than just a checklist; it is a strategic framework. It compels your organization to systematically review various aspects of its operations, from financial reporting processes to IT security and regulatory compliance. By documenting potential risks and existing controls in a standardized format, you ensure consistency across different departments and over time, making it easier to track progress and demonstrate due diligence to auditors or regulatory bodies. It really helps bring clarity to what can otherwise feel like an overwhelming task.
Furthermore, utilizing a consistent internal control risk assessment template helps embed risk awareness into your organizational culture. When teams regularly engage with the assessment process, they become more attuned to potential threats and more proactive in suggesting improvements. This collaborative approach not only strengthens your control environment but also empowers employees to take ownership of risk management, contributing to a more resilient and secure operational landscape. It moves the focus from blame to prevention and continuous improvement.
Key Elements of an Effective Template
An effective template isn’t just a blank sheet; it’s designed to guide you through a comprehensive analysis. It should prompt you to think critically about every facet of your operations and document your findings clearly.
* Risk Category identification: Grouping risks logically like financial, operational, compliance, or strategic.
* Specific Risk Description: A clear, concise statement of the potential threat or vulnerability.
* Existing Controls: Details of the current measures in place to mitigate the risk.
* Likelihood Rating: An assessment of how probable it is that the risk will occur, often on a scale.
* Impact Rating: An assessment of the severity of consequences if the risk materializes.
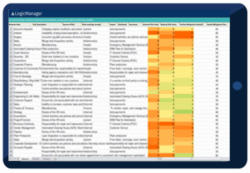
* Risk Score Calculation: A combined score from likelihood and impact to prioritize risks.
* Mitigation Strategies: Proposed actions to reduce the likelihood or impact of the risk.
* Responsible Party: The individual or team assigned to implement and monitor mitigation efforts.
* Review Date: A schedule for re-evaluating the risk and the effectiveness of controls.
Building Your Own Internal Control Risk Assessment Framework
Developing or adapting an internal control risk assessment template that truly fits your organization’s unique needs is a journey, not a sprint. It starts with a foundational understanding of your business objectives. What are you trying to achieve? What processes are critical to those achievements? Once you have a clear picture of your core operations and strategic goals, you can then begin to identify the potential obstacles that could stand in your way. This initial scoping phase is crucial because it ensures your risk assessment is relevant and focused on what truly matters to your success.
The next step involves a comprehensive identification of risks across all relevant areas of your business. This isn’t just about financial risks; it encompasses operational risks like process failures, human error, or supply chain disruptions; compliance risks related to laws and regulations; and even strategic risks concerning market changes or competitive pressures. Engaging various stakeholders from different departments in this brainstorming process can uncover a wider range of potential issues that might otherwise be overlooked. Their diverse perspectives are invaluable.
After identifying the risks, the focus shifts to evaluating the controls you already have in place. Are these controls effective? Do they adequately mitigate the identified risks? This often requires a critical review of policies, procedures, technology systems, and even the human element within your processes. It is not uncommon to discover that some controls are outdated, poorly enforced, or simply not robust enough to address current threats. This phase is about honest self-assessment, not just checking boxes.
Finally, with risks identified and controls assessed, you can then develop action plans for any unacceptable residual risks. This means deciding what further steps are needed to bring risks down to an acceptable level. Whether it involves implementing new controls, enhancing existing ones, transferring the risk through insurance, or even accepting a low-impact risk, each decision should be deliberate and documented. Regular monitoring and review of these action plans are essential to ensure their ongoing effectiveness and to adapt to new or emerging threats.
Implementing a structured approach to risk assessment, perhaps starting with a robust internal control risk assessment template, isn’t a one-time task; it’s an ongoing commitment to organizational health and resilience. It equips your business with the foresight to anticipate challenges, the tools to manage them effectively, and the confidence to pursue your objectives knowing you’re well-prepared. By consistently refining your risk management practices, you build a stronger, more adaptable organization ready to face whatever the future holds.
Embracing this proactive stance means transforming potential weaknesses into opportunities for improvement. It fosters a culture of continuous learning and vigilance, where every team member understands their role in safeguarding the business. Ultimately, this dedication to sound internal controls and regular risk assessment contributes significantly to long-term stability, growth, and the achievement of your strategic vision.