Navigating the complex landscape of information security can feel like trying to solve a puzzle with missing pieces. Every organization, regardless of its size or industry, faces a unique set of digital threats and vulnerabilities that could potentially disrupt operations, compromise sensitive data, or damage its reputation. Understanding and mitigating these risks isn’t just a good idea; it’s an absolute necessity for survival in today’s interconnected world.
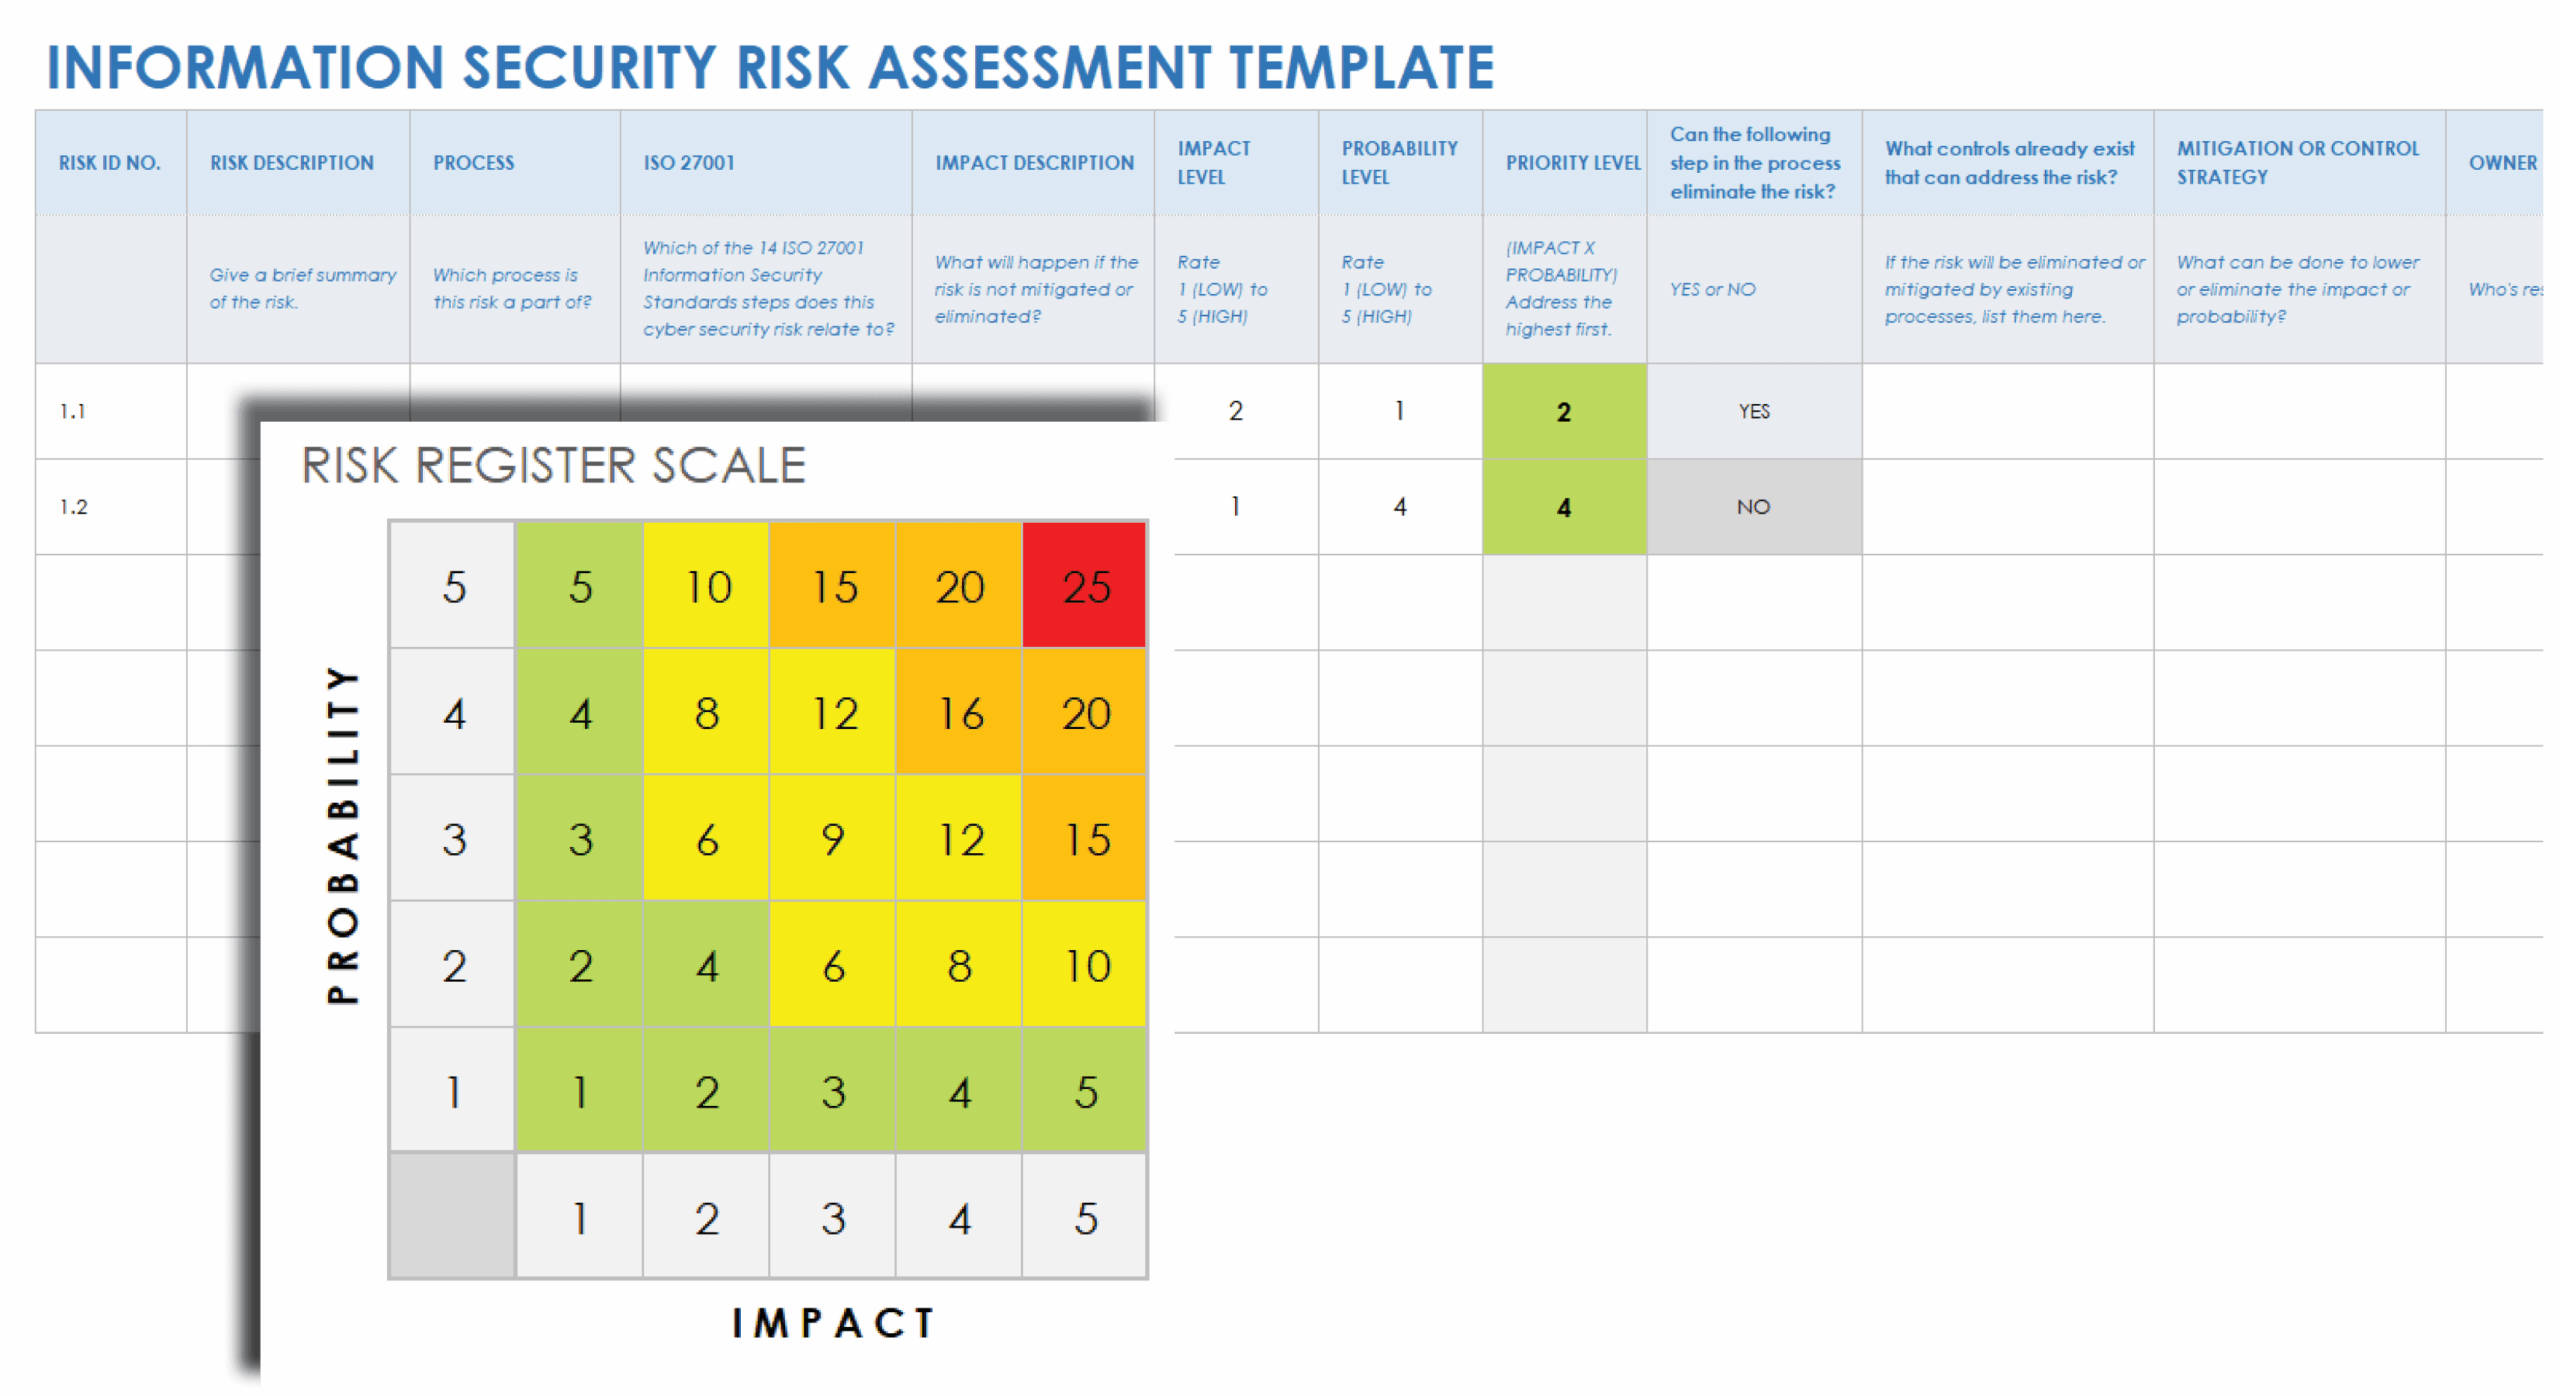
However, approaching information security risk assessment without a structured method can lead to inconsistent results, missed threats, and wasted resources. That’s where a well-designed tool comes into play, offering clarity and a systematic approach. Imagine having a clear roadmap to identify, analyze, and prioritize your security challenges. This foundational tool, the information security risk assessment template, empowers teams to conduct thorough evaluations consistently, ensuring no critical stone is left unturned and that protective measures are strategically aligned with actual risks.
The Critical Role of an Information Security Risk Assessment Template
An information security risk assessment template is much more than just a document; it’s a strategic asset that guides an organization through the intricate process of identifying, analyzing, and evaluating potential information security risks. Think of it as your blueprint for understanding where your digital assets are vulnerable, what threats they face, and what the potential impact of a security incident could be. Without such a structured approach, assessments can become ad-hoc, leading to gaps in coverage and an incomplete picture of your security posture.
The primary advantage of employing a standardized template lies in its ability to bring consistency and objectivity to the risk management process. It ensures that every assessment follows the same methodology, regardless of who is conducting it or when it’s performed. This standardization is crucial for comparing results over time, tracking improvements, and making informed decisions about resource allocation for security initiatives. It transforms what could be an overwhelming task into a manageable and repeatable process.
Furthermore, a comprehensive information security risk assessment template helps organizations meet various compliance requirements. Many regulatory frameworks, such as GDPR, HIPAA, and ISO 27001, mandate regular risk assessments. Using a template ensures that all necessary data points are collected and documented, providing a clear audit trail that demonstrates due diligence. It acts as a verifiable record of your efforts to protect information assets, which is invaluable during audits or in the event of a security breach.
Beyond compliance, the insights gained from using a robust template directly contribute to stronger decision-making. By systematically identifying assets, threats, vulnerabilities, likelihoods, and impacts, the template helps quantify risk levels. This quantification allows management to prioritize risks based on their potential severity and the probability of occurrence, enabling a more efficient and effective allocation of resources to implement appropriate security controls. It moves security conversations from abstract concerns to data-driven strategies.
Key Elements Your Template Should Include
- Asset Identification and Valuation: What information assets do you have (data, systems, hardware, software) and what is their business value?
- Threat Sources: Who or what could pose a threat to your assets (malware, human error, natural disasters, malicious actors)?
- Vulnerabilities: What weaknesses exist in your systems, processes, or people that could be exploited by threats?
- Likelihood and Impact Assessment: How likely is a threat to exploit a vulnerability, and what would be the business impact if it did?
- Risk Rating: A method to quantify and prioritize identified risks (e.g., high, medium, low).
- Existing Controls and Gaps: What security measures are currently in place, and where are the weaknesses?
- Recommended Controls and Action Plan: Specific steps to mitigate or reduce identified risks, along with responsible parties and timelines.
Implementing Your Information Security Risk Assessment Template Effectively
Simply having an excellent information security risk assessment template isn’t enough; its true value comes from its effective implementation. The process begins with clearly defining the scope of your assessment. Are you evaluating a specific system, an entire department, or the organization as a whole? A well-defined scope ensures that the assessment remains focused and manageable, preventing scope creep and ensuring that relevant areas are thoroughly examined. It’s important to involve key stakeholders from IT, legal, operations, and management from the outset to ensure buy-in and gather comprehensive insights.
Once the scope is established, the next critical step involves gathering data. This includes inventories of information assets, network diagrams, system configurations, existing security policies, and any previous incident reports. The more detailed and accurate the data, the more precise your risk analysis will be. Leveraging automated tools for vulnerability scanning and asset discovery can significantly streamline this data collection phase, complementing manual reviews and interviews with personnel who have firsthand knowledge of daily operations and potential weak points.
After data collection, the core of the risk assessment involves systematically analyzing the identified threats, vulnerabilities, and potential impacts. This is where the structure of your template truly shines, guiding you through the process of assigning likelihoods and impact levels, and ultimately calculating a risk rating for each identified scenario. Don’t be afraid to leverage qualitative and quantitative methods to gain a holistic view. The goal here is not just to list risks, but to understand their potential consequences and prioritize them based on your organization’s risk appetite.
Finally, the assessment culminates in developing actionable recommendations for risk treatment. These recommendations should outline specific security controls or strategies to mitigate, transfer, avoid, or accept each identified risk. Each recommendation should include details such as the responsible party, target completion date, and the expected reduction in risk. Regular review cycles, ideally on an annual basis or after significant changes to your IT environment, are essential to keep your risk posture current and responsive to evolving threats. This iterative approach ensures that your security efforts remain agile and effective.
- Foster Collaboration: Involve various departments to get a complete picture of assets and processes.
- Be Realistic: Acknowledge that eliminating all risks is impossible; focus on managing them effectively.
- Document Everything: Maintain clear records of your findings, decisions, and implemented controls.
- Regularly Update: Information security is dynamic; your template and assessments should evolve with it.
- Communicate Clearly: Translate technical findings into business language for management to understand and support.
Embracing a structured approach to information security risk assessment is no longer optional; it’s a cornerstone of robust organizational resilience. By consistently applying a well-designed template, organizations gain unparalleled clarity into their security landscape, transforming potential chaos into a manageable framework. This systematic process not only helps in proactively identifying and addressing weaknesses but also fosters a culture of security awareness and responsibility across all levels.
The journey towards a more secure future is ongoing, characterized by continuous improvement and adaptation. Equipping your team with the right tools and a clear methodology is the most effective way to navigate this journey successfully. It allows you to build stronger defenses, make smarter security investments, and ultimately protect your most valuable assets in an increasingly digital world.