Navigating the complexities of modern digital environments requires more than just good intentions it demands a proactive and structured approach to security. In an age where data breaches and cyberattacks are increasingly common, understanding and mitigating risks to your information systems is not just a best practice it is an absolute necessity for survival and growth. Without a clear picture of potential vulnerabilities and threats, businesses are essentially operating blind, leaving their most valuable assets exposed.

This is where a robust information system risk assessment template becomes an indispensable tool. It transforms an often daunting and abstract task into a manageable, step by step process, helping organizations systematically identify, analyze, and evaluate potential risks. By providing a consistent framework, a template ensures that no critical area is overlooked, allowing you to develop targeted strategies that genuinely enhance your security posture and protect your digital infrastructure.
Why a Robust Risk Assessment is Crucial for Your Business
In today’s interconnected world, businesses face an ever evolving landscape of threats, from sophisticated phishing attacks and ransomware to insider threats and natural disasters. These aren’t just theoretical concerns they can lead to significant financial losses, reputational damage, legal liabilities, and operational downtime. Trying to address these risks reactively often proves to be far more costly and disruptive than implementing preventative measures. A well executed risk assessment is your first line of defense, shining a light on where your vulnerabilities lie before malicious actors or unforeseen events exploit them.
A structured approach ensures that you are not just guessing at your security needs but are making informed decisions based on a clear understanding of your specific risk profile. It moves beyond generic security advice, allowing you to tailor your defenses to the unique characteristics of your information systems and business operations. This strategic insight is invaluable for allocating limited resources effectively, ensuring that your security investments provide the maximum possible protection where it is needed most.
Key Steps in a Thorough Risk Assessment
To truly understand and mitigate your risks, a systematic process is essential. A good information system risk assessment template typically guides you through these fundamental stages:
- Asset Identification: Pinpointing all your valuable information assets, from data and software to hardware and personnel, and understanding their importance.
- Threat Identification: Recognizing potential sources of harm, such as cybercriminals, disgruntled employees, or system failures.
- Vulnerability Identification: Discovering weaknesses in your systems or processes that could be exploited by threats.
- Impact Assessment: Evaluating the potential consequences if a threat exploits a vulnerability, including financial, operational, and reputational damage.
- Likelihood Determination: Estimating the probability of a specific threat exploiting a specific vulnerability.
- Risk Prioritization: Ranking risks based on their calculated likelihood and impact, allowing you to focus on the most critical areas first.
By meticulously following these steps, you gain a comprehensive view of your current security standing. This enables you to move beyond simply identifying problems to actually quantifying them, providing the data needed to make compelling arguments for security investments and policy changes. Understanding the potential impact and likelihood of various risks allows you to prioritize effectively, tackling the most dangerous threats before they materialize into actual incidents.
This structured understanding of your risks empowers you to make strategic decisions about risk treatment, whether that involves mitigating the risk through new controls, transferring it via insurance, avoiding it by ceasing certain activities, or simply accepting it if the cost of mitigation outweighs the potential impact. It also serves as a crucial component for demonstrating due diligence to regulators, auditors, and customers, reinforcing trust and confidence in your organization’s commitment to security.
Crafting Your Own Information System Risk Assessment Template
While many excellent examples exist, the most effective information system risk assessment template is one that is specifically tailored to your organization’s unique environment, industry, and compliance requirements. Generic templates can be a great starting point, but they often need customization to truly reflect the nuances of your business processes, technology stack, and regulatory obligations. Thinking about your specific context as you develop or adapt a template ensures its relevance and utility.
A good template should be intuitive, easy to use, and designed for repeatability. It should guide users through the assessment process logically, from defining the scope of the assessment to documenting findings and recommending remediation actions. The goal is to create a living document that can be regularly updated and reviewed, reflecting the dynamic nature of both your information systems and the threat landscape. This continuous cycle of assessment and improvement is key to maintaining a resilient security posture.
When designing or choosing your information system risk assessment template, consider including dedicated sections for key elements that facilitate a thorough review. Think about categories that will capture all necessary details.
It might include:
- Scope definition: Clearly outlining which systems, data, and processes are included in the assessment.
- Asset inventory: A detailed list of all information assets being evaluated, along with their owners and criticality.
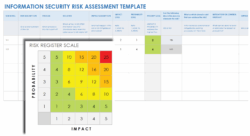
- Risk register: A central log documenting identified risks, their analysis, and current risk levels.
- Control framework: Details on existing security controls and how they mitigate identified risks.
- Action plan: A section for proposed mitigation strategies, responsibilities, and timelines.
- Review schedule: A plan for how often the assessment will be updated and reviewed to maintain its accuracy.
This structured approach not only helps you conduct the assessment but also simplifies future audits and compliance checks. It provides a clear, defensible record of your risk management efforts. Remember, an information system risk assessment template is not a one time project but a continuous process. Regular reviews and updates are essential to ensure that your risk management program remains effective against new threats and evolving business needs. It is through this sustained effort that real and lasting security improvements are achieved, safeguarding your organization for the long term.
Adopting a systematic approach to identifying and managing risks to your information systems is no longer optional it is a fundamental pillar of responsible business operations. By leveraging a well structured framework, organizations can move beyond reactive problem solving to proactive risk mitigation, building a foundation of resilience that protects against potential disruptions. This forward thinking strategy not only secures valuable data and infrastructure but also fosters trust among customers, partners, and stakeholders.
Implementing a consistent, repeatable process for evaluating your security posture empowers your organization to make smarter, data driven decisions about where to invest your resources and how to strengthen your defenses. It is about creating an ongoing dialogue around security, ensuring that risk management is embedded into the fabric of your business rather than being an afterthought. Ultimately, a robust risk assessment framework provides the clarity and direction needed to navigate the digital world with confidence, securing your future in an ever changing threat landscape.