In today’s interconnected world, where digital footprints are expanding daily and physical security remains a constant concern, safeguarding your assets and operations has never been more critical. Businesses of all sizes face an evolving landscape of threats, from sophisticated cyber attacks to natural disasters and internal vulnerabilities. Understanding these potential dangers and their implications isn’t just a good practice; it’s essential for survival and sustained growth.

Navigating this complex environment can feel overwhelming, but it doesn’t have to be. The key lies in adopting a systematic and proactive approach to identify, analyze, and mitigate risks before they escalate into costly incidents. This is where a well-structured framework becomes your indispensable ally, providing clarity and direction in what might otherwise seem like an insurmountable challenge.
Why a Structured Approach to Security is Non-Negotiable
Many organizations operate with a reactive mindset when it comes to security, only addressing issues after a breach or incident has occurred. This “fix it when it breaks” approach is not only expensive in terms of recovery costs and reputational damage but also leaves critical assets exposed for extended periods. Without a predefined methodology, it’s easy to miss subtle vulnerabilities or overlook entire categories of threats, creating blind spots that attackers are all too eager to exploit. A structured approach, on the other hand, allows you to systematically examine your environment and build robust defenses.
A comprehensive assessment involves several crucial steps. First, you need to identify all your valuable assets, whether they are physical hardware, sensitive data, intellectual property, or even your brand’s reputation. Next, you must pinpoint potential threats that could harm these assets, ranging from human error and malicious insiders to external cybercriminals and natural disasters. Finally, you analyze the vulnerabilities within your systems and processes that these threats could exploit, assessing the likelihood of an event and its potential impact.
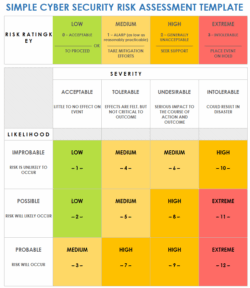
This is precisely where a dedicated security threat and risk assessment template proves invaluable. It provides a standardized framework that guides you through each step of the identification and analysis process, ensuring that no stone is left unturned. By following a consistent format, you can maintain thoroughness across different departments or projects, making it easier to compare risks, prioritize mitigation efforts, and communicate findings clearly to all stakeholders. It transforms a daunting task into a manageable series of actions.
Furthermore, using a template brings a level of consistency and repeatability to your risk management efforts. It helps ensure that every assessment is conducted with the same rigor and attention to detail, regardless of who is performing it. This not only improves the quality of your risk insights but also facilitates easier updates and reviews as your organization evolves and new threats emerge. It turns security into an ongoing, integrated part of your business operations rather than an infrequent, isolated event.
Key Elements Your Assessment Should Cover
- Asset Identification clearly defining what you need to protect and its value
- Threat Sources and Events outlining who or what might cause harm and how
- Vulnerability Analysis pinpointing weaknesses in your systems or processes
- Impact Assessment evaluating the potential consequences if a risk materializes
- Likelihood Determination estimating the probability of a threat exploiting a vulnerability
- Risk Level Calculation combining impact and likelihood to determine overall risk
- Mitigation Strategies detailing actions to reduce or eliminate identified risks
- Residual Risk Review reevaluating risks after mitigation efforts are implemented
Building Your Effective Security Threat and Risk Assessment Template
Transitioning from understanding the “why” to implementing the “how” requires a practical tool. While many off-the-shelf templates exist, the most effective security threat and risk assessment template is often one you either customize to your specific organizational needs or build from the ground up with your context in mind. This customization ensures that the template speaks directly to your unique operational environment, regulatory requirements, and risk appetite, making it far more relevant and actionable than a generic solution.
The journey begins with gathering the right information. Before you can even start filling in threat details, you need a comprehensive understanding of your current state. This includes creating an inventory of all your information technology assets, physical infrastructure, critical business processes, and the data they handle. Additionally, document any existing security controls, compliance obligations like GDPR or HIPAA, and previous security incidents or audit findings. This foundational data will populate the initial sections of your template and provide the context for all subsequent analysis.
Risk assessment is not a one-time event; it is an iterative process that requires regular review and updates. Your template should be designed to support this ongoing cycle. Think of it as a living document that reflects changes in your threat landscape, technological advancements, and business priorities. Scheduling periodic reviews, perhaps quarterly or annually, ensures that your template remains relevant and that your risk posture is continuously aligned with your organizational goals. This continuous refinement helps maintain an adaptive and resilient security program.
Moreover, a well-designed template serves as a powerful communication tool, fostering collaboration across various departments. By standardizing how risks are identified, analyzed, and presented, it enables clearer discussions among IT, management, legal, and operational teams. Everyone can speak the same language when it comes to security, understand their roles in risk mitigation, and contribute to a unified security strategy. This shared understanding and collective responsibility are crucial for building a strong security culture throughout your organization.
Implementing a structured approach to identifying and managing potential security threats is paramount for any organization aiming for resilience and continuity. By leveraging a comprehensive security threat and risk assessment template, you gain a clear, actionable roadmap to navigate the complexities of modern security challenges, moving beyond reactive fixes to proactive protection. It empowers you to make informed decisions, allocate resources wisely, and build a more secure future.
Ultimately, having a robust framework in place allows you to not only protect your valuable assets but also build trust with your customers, comply with regulations, and maintain your competitive edge. Investing time in developing or adapting a solid security threat and risk assessment template is an investment in your organization’s longevity and peace of mind, transforming abstract concerns into manageable, actionable insights for lasting security.