Navigating the complex world of rules and regulations can feel like walking through a minefield. For any organization, regardless of its size or industry, ensuring compliance isn’t just a good practice; it’s a fundamental necessity to avoid significant penalties, reputational damage, and operational disruptions. The sheer volume and ever-changing nature of these mandates make proactive management indispensable.
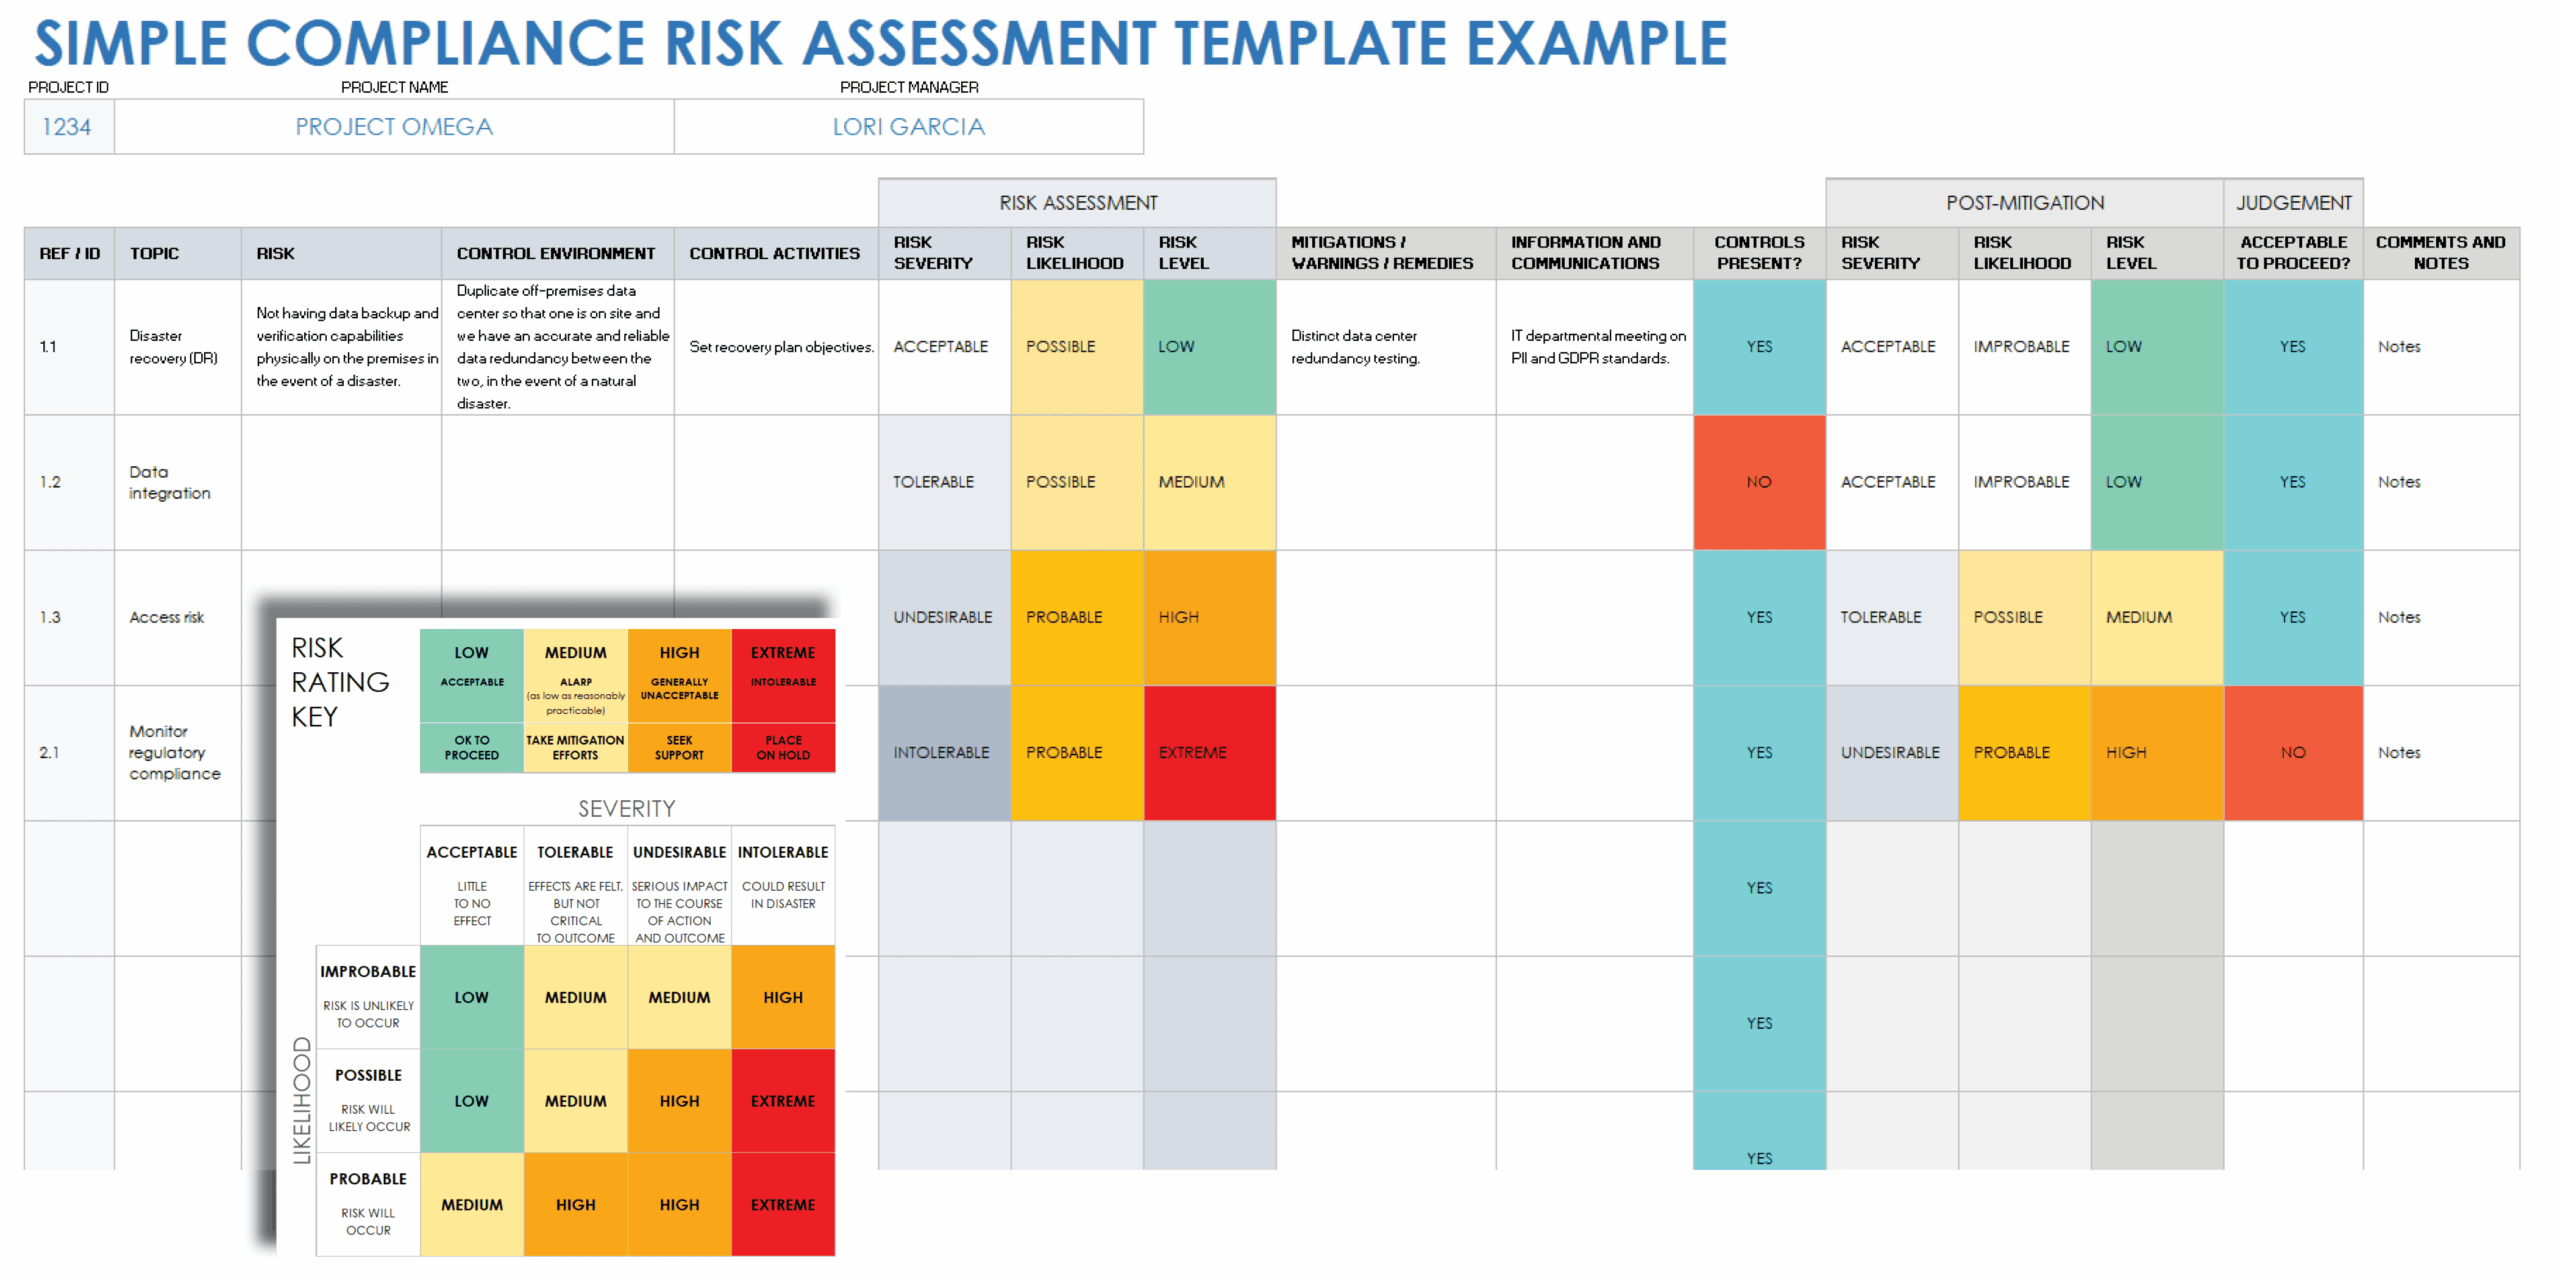
That’s where a structured approach comes into play. Having a clear, repeatable process to identify, evaluate, and mitigate potential non-compliance issues is paramount. A well-designed regulatory compliance risk assessment template acts as your essential guide, helping you systematically tackle these challenges and build a robust compliance framework that protects your business from unnecessary exposure.
Understanding Regulatory Compliance Risk Assessment and Its Importance
A regulatory compliance risk assessment is essentially a systematic process designed to identify potential areas where an organization might fail to meet its legal, industry, or internal obligations. It involves evaluating the likelihood of these failures occurring and the potential impact they could have. Think of it as your company’s early warning system, allowing you to spot potential issues before they escalate into costly problems. This proactive stance is far more effective and less expensive than reacting to a crisis after the fact.
Why is this so crucial? Firstly, the financial implications of non-compliance can be staggering. Fines from regulatory bodies can range from thousands to millions, often accompanied by legal fees and potential compensation payments. Beyond the direct financial hit, there’s the invaluable asset of reputation. A single compliance misstep can severely damage public trust, erode customer loyalty, and make it difficult to attract new talent or partners. In today’s interconnected world, news travels fast, and a tarnished image can take years, if not decades, to repair.
Moreover, conducting regular risk assessments helps foster a culture of compliance throughout your organization. When employees understand the risks involved and the importance of adhering to regulations, they become more vigilant and accountable. It moves compliance from being seen as a bureaucratic burden to an integral part of how the business operates ethically and effectively. Ultimately, it allows your leadership team to make informed decisions about resource allocation, focusing efforts where the risk is highest and the potential impact most severe.
Key Stages of the Assessment Process
- Identify Regulatory Obligations: Understand all the laws, regulations, industry standards, and internal policies that apply to your organization’s operations, products, and services. This often involves legal counsel and subject matter experts.
- Assess Risks: For each identified obligation, determine what could go wrong. What are the specific scenarios that could lead to non-compliance? Consider both internal factors (e.g., process gaps, employee training) and external factors (e.g., changing regulations).
- Evaluate Controls: Analyze the existing controls or safeguards you have in place to prevent or detect non-compliance. Are they effective? Are there gaps? This might include policies, procedures, technological solutions, and training programs.
- Determine Likelihood and Impact: For each risk, estimate how likely it is to occur and what the severity of the consequences would be if it did. This helps prioritize risks, focusing on those with high likelihood and high impact.
- Develop Mitigation Plans: For high-priority risks, outline specific actions to reduce their likelihood or impact. This could involve implementing new controls, updating policies, providing additional training, or seeking expert advice.
- Monitor and Review: Compliance is not a static state. Regulations change, business operations evolve, and new risks emerge. Regularly review and update your assessment, ensuring it remains relevant and effective over time.
Leveraging a Regulatory Compliance Risk Assessment Template for Success
Using a comprehensive regulatory compliance risk assessment template transforms what could be a daunting, ad-hoc process into a streamlined, consistent, and manageable task. It provides a standardized framework, ensuring that all relevant areas are considered and that assessments are conducted uniformly across different departments or business units. This consistency is crucial for generating comparable data and making informed, organization-wide decisions about risk management strategies. Without such a template, you might inadvertently overlook critical areas, leading to gaps in your compliance posture.
The structure offered by a template guides you through each step, prompting you to consider various aspects of risk, from identification to mitigation. It encourages a structured dialogue among stakeholders, fostering collaboration between legal, operations, IT, and other relevant teams. This cross-functional input is vital because compliance risks often span multiple departments, and a holistic view is necessary for effective management. For instance, a data privacy regulation might impact IT infrastructure, marketing practices, and HR data handling, all of which need to be assessed collectively.
Furthermore, a robust regulatory compliance risk assessment template serves as an invaluable record-keeping tool. It documents your risk identification process, the controls you have in place, and the actions you’re taking to address identified weaknesses. This documentation is not only essential for internal audit purposes but also provides tangible evidence of due diligence should you ever face an inquiry from a regulatory body. Demonstrating that you have a proactive and systematic approach to compliance can be as important as the outcome itself.
Think of the template not as a static document to be filled out once and forgotten, but as a living instrument that evolves with your business and the regulatory landscape. Regular updates and reviews ensure its continued relevance and effectiveness. It facilitates ongoing monitoring, allowing you to track the progress of mitigation actions and reassess risks as conditions change. This iterative process is the hallmark of a mature and resilient compliance program.
Essential Elements of a Robust Template
- Risk ID: A unique identifier for each specific risk.
- Regulatory Area/Obligation: Clearly state the specific law, regulation, or standard the risk pertains to.
- Risk Description: Detail what the non-compliance risk is and how it might occur.
- Potential Impact: Describe the consequences (financial, reputational, operational) if the risk materializes.
- Likelihood: Assign a probability rating (e.g., Low, Medium, High).
- Existing Controls: List current measures in place to mitigate the risk.
- Control Effectiveness: Rate how well current controls are working.
- Residual Risk Rating: The risk level remaining after existing controls are considered.
- Mitigation Actions/Recommendations: Specific steps to further reduce the risk.
- Action Owner: The person or team responsible for implementing mitigation.
- Target Completion Date: Deadline for mitigation actions.
- Status: Current progress of mitigation efforts.
- Review Date: When the risk and its mitigation will be re-evaluated.
Ultimately, implementing a well-structured approach to managing regulatory risks isn’t just about avoiding penalties; it’s about building a more resilient, ethical, and trustworthy organization. By consistently using a thoughtful template, you’re not just checking boxes; you’re actively shaping a culture where compliance is integrated into every decision and action. This proactive stance ensures long-term stability and positions your business for sustained success in an ever-changing regulatory environment.