In today’s fast-paced digital world, data is often called the new oil – a vital resource that fuels decisions, drives innovation, and ensures operational efficiency. But just like oil, raw data needs to be refined and protected to deliver its true value. This protection hinges on something called data integrity, which essentially means keeping your data accurate, consistent, and reliable throughout its entire lifecycle. Without it, even the most advanced analytics or business intelligence tools will be built on shaky ground, leading to misguided strategies and potentially costly errors.

Understanding and managing the risks to this crucial data integrity is not just good practice; it’s a fundamental requirement for any organization operating in the modern landscape. That’s where a structured approach comes into play. By systematically identifying, evaluating, and mitigating potential threats to your data’s accuracy and consistency, you can safeguard your most valuable digital assets. A well-designed data integrity risk assessment template serves as your roadmap, guiding you through this complex process and ensuring no critical stone is left unturned.
Why a Data Integrity Risk Assessment is Essential
Imagine making critical business decisions based on faulty or incomplete information. The repercussions could range from financial losses and operational inefficiencies to reputational damage and legal penalties. Data integrity risks aren’t abstract; they manifest in real-world scenarios, whether it’s an accidental data entry error, a malicious cyberattack corrupting your databases, or a system malfunction altering crucial records. A proactive data integrity risk assessment allows you to pinpoint these vulnerabilities before they escalate into significant incidents.
Beyond simply avoiding negative outcomes, a robust risk assessment fosters a culture of data quality within your organization. It helps teams understand the value of the data they handle and the importance of adhering to best practices. By clearly defining roles, responsibilities, and procedures, you build a stronger defense against both human error and sophisticated threats. This isn’t just about security; it’s about establishing trust in your data at every level of your business operations.
Furthermore, regulatory compliance is a significant driver for conducting thorough data integrity assessments. Industries from pharmaceuticals (GxP) to finance (SOX) and healthcare (HIPAA), as well as general data protection regulations like GDPR, mandate strict controls over data accuracy and consistency. Failing to meet these standards can result in hefty fines and severe legal consequences. A structured assessment demonstrates due diligence and helps ensure you meet or exceed these regulatory requirements, protecting your organization from potential sanctions.
Ultimately, investing time in a comprehensive data integrity risk assessment is an investment in your organization’s long-term stability and success. It empowers you to make informed decisions about resource allocation for data protection, prioritize mitigation efforts, and continuously improve your data governance framework. It’s about moving from a reactive stance, where you’re constantly putting out fires, to a proactive one, where you anticipate and prevent them.
Key Areas Your Assessment Should Cover
- Data Input and Creation: How data enters your systems, including manual entry, automated feeds, and external sources.
- Data Storage and Management: The databases, cloud platforms, and physical storage where data resides, and how it’s organized.
- Data Processing and Transformation: Any operations, calculations, or changes made to data, and the systems that perform them.
- Data Transmission: How data moves between systems, departments, or external parties.
- Data Retention and Archiving: Policies and practices for how long data is kept and how it’s securely retired or archived.
- Access Controls and User Management: Who has permission to view, edit, or delete data, and how those permissions are managed.
- Audit Trails and Logging: The mechanisms for tracking changes to data and user activities.
Building Your Own Data Integrity Risk Assessment Template
While generic templates can offer a starting point, the most effective data integrity risk assessment template will be one tailored to your specific organizational context, industry regulations, and unique data landscape. This isn’t a one-size-fits-all endeavor. Begin by clearly defining the scope of your assessment – are you looking at a specific system, a department, or your entire enterprise? What are the critical data sets that, if compromised, would pose the greatest risk to your business?
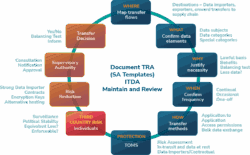
The process of building and utilizing such a template typically follows several distinct phases. It starts with identifying all relevant data assets and the processes that interact with them. From there, you move into pinpointing potential threats, which can range from human error and software bugs to cyberattacks and natural disasters, and the vulnerabilities within your systems that these threats could exploit. Once threats and vulnerabilities are identified, the next step involves analyzing the likelihood of these events occurring and the potential impact they would have on your business.
Following this analysis, you’ll evaluate the level of risk associated with each identified scenario, often by mapping likelihood against impact. This allows you to prioritize which risks need immediate attention and which can be addressed with less urgency. The core of any effective risk assessment lies in developing robust mitigation strategies for each significant risk. These strategies could include implementing new security controls, enhancing existing data validation procedures, improving employee training, or updating backup and recovery protocols.
Remember, a data integrity risk assessment isn’t a one-time project. It’s an ongoing commitment. Your organization’s data environment is constantly evolving, with new systems, processes, and threats emerging regularly. Therefore, your template should also incorporate provisions for periodic review and continuous monitoring. This ensures that your controls remain effective and that you’re always adapting to the changing risk landscape. Think of your data integrity risk assessment template as a living document, evolving alongside your business.
- Define Scope and Objectives: Clearly articulate what data, systems, and processes are included and the goals of the assessment.
- Identify Data Assets and Processes: Catalog all critical data and the workflows that create, store, process, and transmit it.
- Pinpoint Potential Threats and Vulnerabilities: List all possible events that could compromise data integrity and the weaknesses in your systems.
- Assess Impact and Likelihood: Quantify the potential damage if a risk materializes and the probability of it happening.
- Determine Risk Level: Combine impact and likelihood to assign a risk score or category.
- Outline Mitigation Strategies: Develop specific actions to reduce or eliminate identified risks.
- Establish Review and Monitoring Cycles: Plan for regular reassessments and continuous oversight of data integrity controls.
Embracing a systematic approach to data integrity isn’t merely about compliance; it’s about fostering trust in your information and enabling truly data-driven decision-making. By meticulously identifying, analyzing, and addressing potential weaknesses, you empower your organization to operate with greater confidence and resilience in an increasingly data-dependent world.
Taking the initiative to develop and regularly update your data integrity risk management framework provides a clear competitive advantage. It helps secure your most valuable digital assets, protects your reputation, and ensures your operations remain robust against an evolving array of challenges. This proactive stance is fundamental to sustained growth and success in the digital age.