Navigating the complex landscape of cybersecurity can feel like a daunting task for any organization, regardless of size or industry. With new threats emerging daily and existing vulnerabilities constantly being exploited, a proactive approach to security is not just recommended, it’s absolutely critical. Understanding where your weaknesses lie and what dangers lurk is the first step towards building a robust defense.

This is where a structured approach becomes invaluable. Instead of guessing or reacting to incidents, a systematic process allows you to identify, evaluate, and mitigate risks before they can cause significant harm. While the idea of performing such an assessment might seem overwhelming, a well-designed framework can simplify the entire endeavor, making it manageable and highly effective.
Why a Threat and Vulnerability Assessment Template is Essential for Your Security Posture
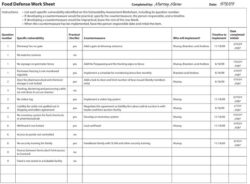
Implementing a comprehensive security strategy requires more than just installing firewalls and antivirus software; it demands a deep understanding of your unique risk profile. A reliable threat and vulnerability assessment template provides the foundational structure needed to achieve this. It guides you through the process of systematically cataloging assets, identifying potential threats, uncovering existing vulnerabilities, and ultimately, calculating the risks that matter most to your business. This structured approach ensures that no critical area is overlooked, offering a consistent methodology that can be applied across different departments or projects within your organization.
Beyond simply identifying weaknesses, a template helps standardize the entire assessment process. Imagine multiple teams conducting security reviews using disparate methods; the results would be difficult to compare, consolidate, or act upon effectively. A standardized threat and vulnerability assessment template ensures that everyone is speaking the same language, using the same criteria, and reporting in a consistent format. This consistency is crucial for generating actionable insights and making informed decisions about resource allocation for security enhancements.
Furthermore, using a pre-defined template significantly reduces the time and effort involved in initiating and conducting assessments. Instead of starting from scratch each time, which can be prone to errors and omissions, you have a clear roadmap. This efficiency not only saves valuable operational time but also allows security teams to focus more on analysis and mitigation rather than on process development. It democratizes the assessment process, making it accessible even to those who might not be security experts but understand their specific operational context.
Ultimately, a structured template fosters a culture of continuous improvement in security. It becomes a living document that evolves with your organization and the threat landscape. By routinely using a consistent framework, you can track progress over time, measure the effectiveness of your mitigation strategies, and adapt your defenses as new threats emerge or business priorities shift. This systematic approach ensures that your security posture is always resilient and responsive.
Key Components of an Effective Template
- Scope Definition: Clearly outlining what systems, data, and processes will be included in the assessment.
- Asset Identification: Cataloging all critical assets, distinguishing between hardware, software, data, and human elements.
- Threat Identification: Listing potential malicious acts, natural disasters, or accidental events that could impact assets.
- Vulnerability Identification: Discovering weaknesses in systems, configurations, or practices that threats could exploit.
- Risk Assessment: Evaluating the likelihood of a threat exploiting a vulnerability and the potential impact of such an event.
- Mitigation Strategies: Documenting recommended controls, actions, and timelines to reduce identified risks.
- Reporting and Tracking: Providing a clear mechanism to document findings, recommendations, and the status of mitigation efforts.
How to Effectively Utilize Your Threat and Vulnerability Assessment Template
Once you have your threat and vulnerability assessment template in hand, the next step is to put it into action effectively. The first stage involves thorough preparation. Before diving into the assessment itself, gather all relevant documentation about your IT infrastructure, business processes, and existing security policies. Assemble a diverse team, involving not only IT and security personnel but also representatives from different departments who understand their specific operational challenges and data sensitivities. This collaborative approach ensures a holistic view of your organizational risks.
Next, begin by clearly defining the scope of your assessment, as guided by the template. Are you focusing on a specific application, an entire network, or a particular data set? Clearly outlining what is in and out of scope prevents scope creep and ensures the assessment remains focused and manageable. Following this, meticulously identify and categorize all relevant assets within that defined scope. The template will prompt you to consider various types of assets, from physical servers and cloud instances to sensitive customer data and critical intellectual property.
With assets identified, move on to the core of threat and vulnerability identification. Use the template’s structured sections to brainstorm potential threats, both internal and external, and then systematically look for vulnerabilities associated with each identified asset. This might involve reviewing configuration files, conducting penetration tests, or simply auditing user access permissions. The template helps ensure that you consider a broad range of weaknesses, from unpatched software and weak authentication protocols to human errors and physical security gaps.
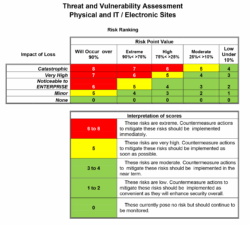
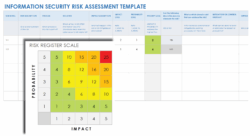
After uncovering threats and vulnerabilities, the template guides you through the risk assessment phase. Here, you’ll evaluate the likelihood of each threat exploiting a vulnerability and the potential impact if it were to occur. This often involves qualitative or quantitative scoring to prioritize risks, allowing you to focus your limited resources on the most critical issues first. Documenting these findings, along with your recommended mitigation strategies, is crucial for turning insights into actionable plans.
A well-executed security assessment using a robust framework offers more than just a snapshot of your current security posture; it empowers your organization to make proactive and informed decisions about its digital defense. By systematically identifying and addressing potential weaknesses, you not only protect valuable assets but also build trust with your customers and stakeholders.
Embracing a structured approach to identifying and mitigating risks is a fundamental step towards cultivating a resilient and secure operational environment. It transforms the abstract concept of cybersecurity into a practical, manageable process, ensuring your organization remains robust against an ever-evolving landscape of threats.