Navigating the intricate landscape of information technology presents a unique set of challenges for any organization. With cyber threats constantly evolving and regulatory requirements becoming more stringent, ensuring your IT infrastructure is secure and compliant is no longer just an option; it’s a necessity. This can often feel like a daunting task, trying to identify every potential vulnerability and understand its impact before it becomes a real problem.
That’s where a structured approach comes into play, providing clarity and efficiency in an otherwise complex process. Imagine having a clear roadmap, a step-by-step guide that helps you systematically evaluate risks, assess controls, and prioritize actions. This is precisely the power of a well-designed it audit risk assessment template, a tool that can transform how your organization manages its digital defenses and ensures operational resilience.
Why an IT Audit Risk Assessment Template is Your Best Friend
In the fast-paced world of technology, relying on ad hoc risk assessments can leave significant gaps in your security posture. An it audit risk assessment template brings a much-needed layer of consistency and thoroughness to the entire process. It ensures that every critical area is examined, from network infrastructure and software applications to data handling and employee access controls, preventing important details from slipping through the cracks due to oversight or varying approaches between different audit teams.
Beyond just consistency, using a template dramatically boosts efficiency. Instead of starting from scratch with each new audit or assessment, your team can leverage a pre-defined structure, saving countless hours that would otherwise be spent on planning and formatting. This allows auditors to focus their valuable time and expertise on the actual assessment of risks and the development of actionable recommendations, rather than on administrative tasks. It also streamlines the review process, as all information is presented in a familiar and standardized format.
Furthermore, a robust template acts as a powerful communication tool. It helps articulate complex IT risks in a clear, understandable manner to both technical and non-technical stakeholders across the organization. When everyone understands the identified risks, their potential impact, and the proposed mitigation strategies, it fosters better decision-making and ensures that risk management efforts are aligned with overall business objectives. It promotes a culture of proactive security, where risk awareness is embedded throughout the organization.
Key Elements You’ll Find in a Comprehensive Template
- Risk Identification: A structured way to list potential threats and vulnerabilities.
- Impact Assessment: Categories and scales to evaluate the potential harm if a risk materializes.
- Likelihood Determination: Methods to estimate the probability of a risk occurring.
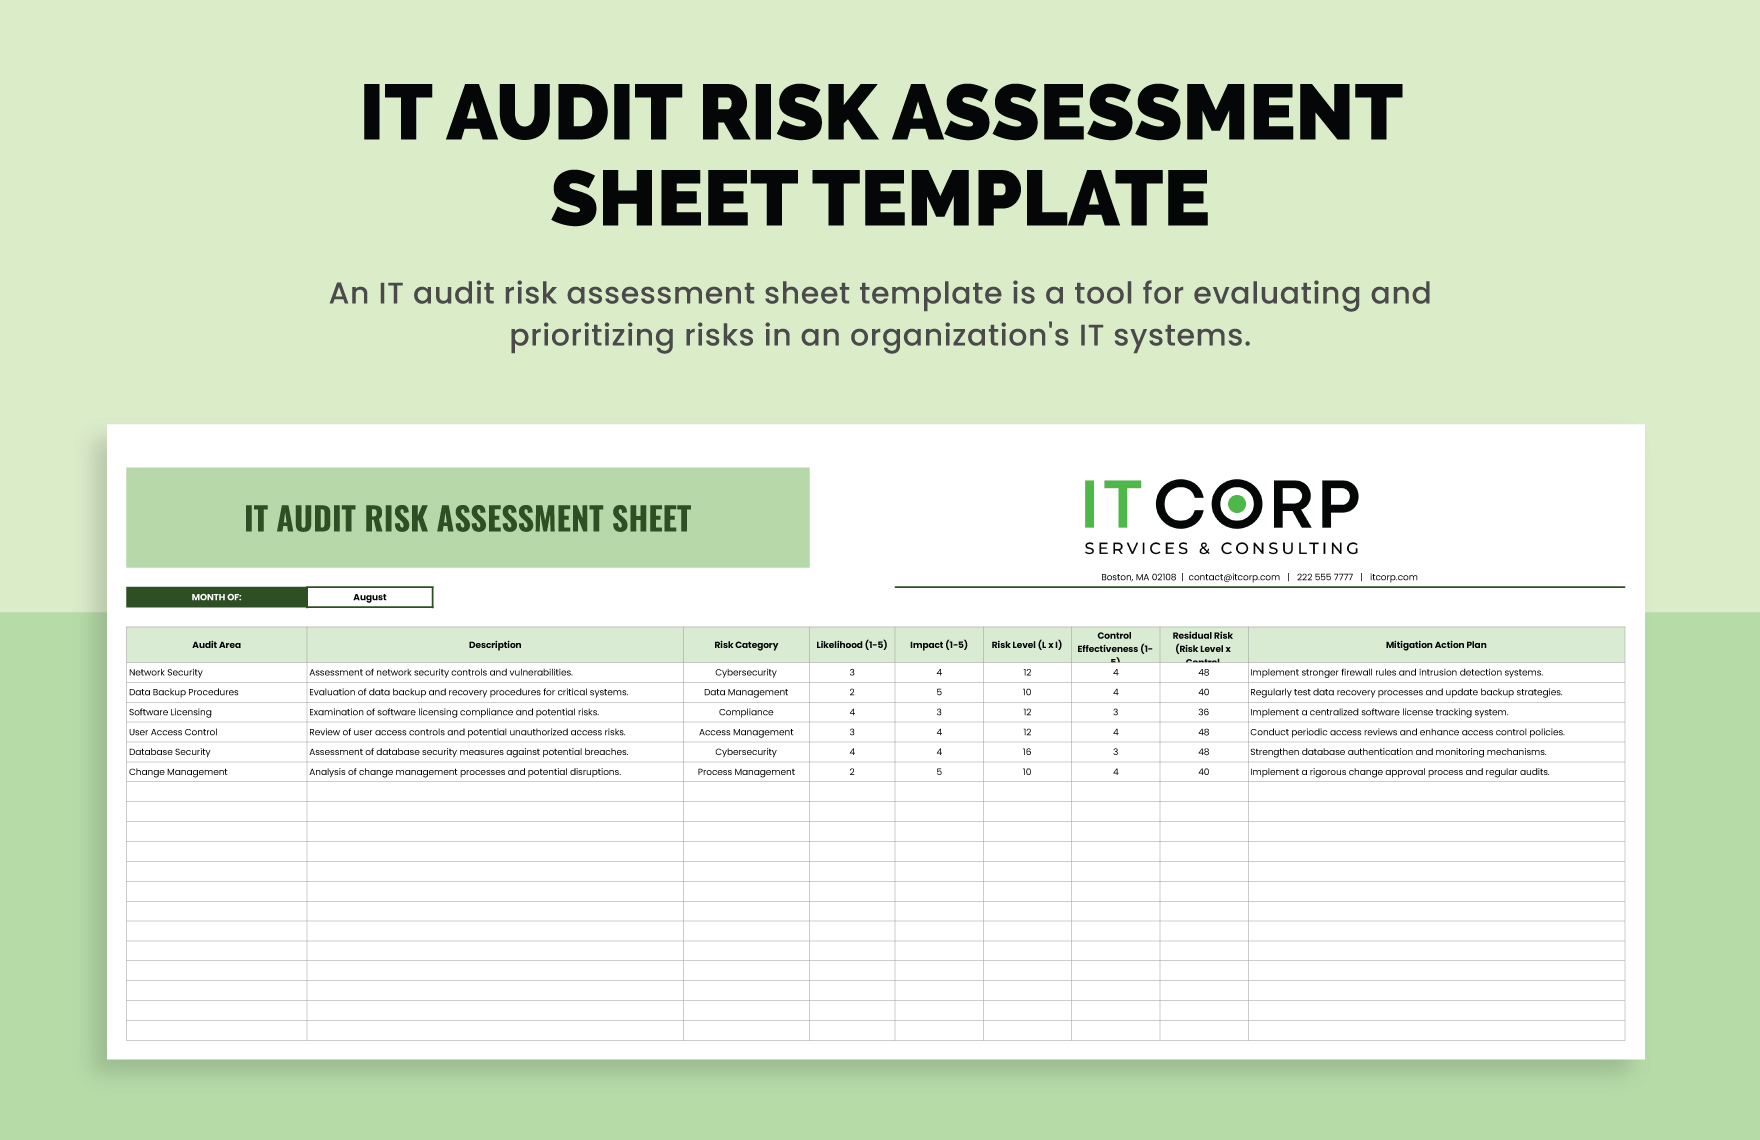
- Control Analysis: Sections to document existing controls and assess their effectiveness.
- Residual Risk Calculation: Tools to determine the remaining risk after controls are applied.
- Mitigation Strategies: Space to outline recommended actions and responsible parties.
- Prioritization Matrix: A system for ranking risks based on their severity and likelihood.
Putting Your Template to Work: A Step-by-Step Guide
Implementing an it audit risk assessment template effectively requires more than just filling in blanks; it demands a thoughtful and systematic approach. The real value comes from how you utilize its structure to drive meaningful insights and protective measures. Begin by clearly defining the scope of your assessment. Are you evaluating a specific system, a particular department, or the entire organizational IT landscape? A well-defined scope ensures that your efforts are focused and that the template’s sections are applied relevantly to the areas under review, preventing scope creep and ensuring a manageable audit.
Once the scope is established, the next crucial step involves gathering the necessary information. This typically includes reviewing existing documentation such as IT policies, network diagrams, previous audit reports, and incident logs. Interviews with key personnel, including IT staff, system owners, and business process owners, are also invaluable. These conversations can reveal practical insights into day-to-day operations and potential weaknesses that might not be evident from documentation alone. The template serves as an excellent guide during these interviews, ensuring all critical questions are asked.
After collecting the data, you’ll move into the core analysis phase, systematically identifying risks, assessing their impact and likelihood, and evaluating existing controls using the framework provided by your template. Be thorough in your analysis, considering both internal and external factors that could influence risks. It’s not enough to simply list a risk; understanding the “why” and “how” behind it allows for more effective mitigation strategies. The structured nature of the template helps maintain objectivity and ensures that the assessment is comprehensive and defensible.
Finally, the template guides you through the process of developing actionable mitigation plans and prioritizing them based on the calculated residual risk. This involves outlining specific recommendations, assigning ownership for each action, and setting realistic timelines for implementation. A good template will also include sections for follow-up and monitoring, emphasizing that risk assessment is not a one-time event but an ongoing cycle of improvement. Regularly revisiting and updating your assessments ensures your organization remains resilient against emerging threats and evolving business needs.
Embracing a structured approach to IT risk assessment is a fundamental step toward building a truly resilient and secure organization. By systematically identifying, evaluating, and mitigating potential threats, you empower your team to make informed decisions that protect vital assets and support strategic objectives. This proactive posture not only safeguards your information systems but also fosters greater confidence among stakeholders, demonstrating a commitment to security and operational excellence.