In today’s interconnected world, keeping your digital assets safe isn’t just a good idea, it’s an absolute necessity. Organizations of all sizes face constant threats from cyber criminals, making proactive measures essential to protect sensitive data and maintain operational continuity. One of the most critical steps in building a robust defense is regularly assessing your vulnerabilities.

However, conducting thorough and consistent vulnerability assessments can feel like a daunting task without a clear roadmap. That’s where a well-structured approach comes into play, providing the guidance needed to systematically identify, evaluate, and mitigate potential weaknesses before they can be exploited.
Why a Structured Template is Your Best Ally in Vulnerability Assessments
Imagine trying to build a complex structure without a blueprint. You might eventually get something standing, but it would likely be inefficient, inconsistent, and prone to collapse. The same principle applies to cyber security vulnerability assessments. Without a structured framework, you risk missing critical areas, producing inconsistent reports, and struggling to track remediation efforts effectively. A dedicated cyber security vulnerability assessment template acts as that essential blueprint, ensuring every step is covered systematically.
A comprehensive template brings a much-needed layer of consistency and efficiency to your security operations. It standardizes the process, making it repeatable and measurable across different teams or assessment periods. This not only saves valuable time but also drastically improves the quality and reliability of your assessment outcomes. You’ll be able to quickly onboard new team members, present clearer findings to stakeholders, and demonstrate due diligence to auditors.
Furthermore, a good template isn’t just a checklist; it’s a living document that evolves with your organization’s security posture and the ever-changing threat landscape. It helps you document your methodologies, record findings with precision, assign risk levels consistently, and propose actionable recommendations for remediation. This structured approach transforms a potentially chaotic process into a streamlined and highly effective one, ultimately strengthening your overall cyber resilience.
By enforcing a uniform approach to data collection and analysis, a template ensures that no stone is left unturned. It helps in maintaining a clear historical record of vulnerabilities, their impact, and the actions taken to address them. This historical data is invaluable for identifying trends, measuring the effectiveness of your security investments, and continuously improving your defense strategies.
Essential Components of a Robust Template
- Executive Summary: A concise overview for non-technical stakeholders.
- Scope and Methodology: Clearly defines what was assessed and how.
- Identified Vulnerabilities: Detailed descriptions of each discovered weakness.
- Risk Rating and Impact: An assessment of potential harm and likelihood of exploitation.
- Recommendations for Remediation: Specific, actionable steps to fix vulnerabilities.
- Timeline and Responsibility: Who is accountable for what and by when.
- Supporting Evidence: Screenshots, logs, or other proofs of findings.
Building Your Own Cyber Security Vulnerability Assessment Template: A Practical Guide
While readily available templates can provide a good starting point, the most effective cyber security vulnerability assessment template is one that is tailored specifically to your organization’s unique environment, regulatory requirements, and risk appetite. Think of it as customizing a high-performance vehicle to suit your particular racing conditions. Generic solutions might get you started, but bespoke adjustments will give you the winning edge. The process of building or adapting your template should be an iterative one, reflecting your evolving infrastructure and the dynamic nature of cyber threats.
Start by reviewing your existing security policies and compliance obligations. What industry standards or regulations (like GDPR, HIPAA, ISO 27001) must you adhere to? Your template should explicitly incorporate sections to address these requirements, ensuring that your assessments not only identify technical weaknesses but also demonstrate compliance with relevant mandates. This integration will make your assessments dual-purpose, serving both security and regulatory needs efficiently.
Next, define the different types of assets you typically assess and the common vulnerability categories relevant to your systems. Whether it’s web applications, network infrastructure, cloud environments, or endpoints, each requires a slightly different focus. Your template should be flexible enough to accommodate these various assessment types, perhaps with modular sections that can be added or removed as needed. This modularity prevents the template from becoming overly cumbersome while still ensuring thoroughness.
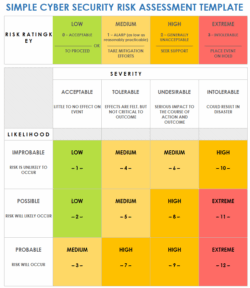
Finally, establish a clear, consistent system for risk scoring and remediation tracking. How will you prioritize vulnerabilities? What criteria will you use to determine severity and impact? A standardized risk matrix, integrated directly into your template, ensures that all findings are evaluated using the same objective measures. This consistency is crucial for making informed decisions about where to allocate resources and which vulnerabilities demand immediate attention. Regularly review and refine your template based on lessons learned from past assessments and emerging threat intelligence.
- Define Your Scope Clearly: What systems, applications, or networks will be included in the assessment?
- Categorize Vulnerabilities: Use a consistent classification system (e.g., OWASP Top 10 for web apps).
- Establish a Consistent Risk Rating System: Implement a severity scale (e.g., Critical, High, Medium, Low) and define its criteria.
- Outline Remediation Steps: Provide practical and clear instructions for fixing identified issues.
- Assign Responsibilities: Clearly indicate who is accountable for addressing each vulnerability.
- Review and Refine Regularly: Update the template to reflect new technologies, threats, and organizational changes.
Adopting a structured template for your vulnerability assessments is more than just a procedural enhancement; it’s a strategic investment in your organization’s long-term security posture. It transforms what could be a sporadic and ad-hoc activity into a consistent, robust program that continuously identifies and addresses weaknesses. This proactive approach minimizes your exposure to cyber risks, strengthens your defenses, and builds greater confidence in your ability to protect valuable assets.
Ultimately, a well-implemented template empowers your security team to work more efficiently, communicate more effectively, and make data-driven decisions that genuinely enhance your cyber resilience. It becomes an indispensable tool in your ongoing battle against an ever-evolving landscape of digital threats, ensuring that your organization remains secure and compliant for years to come.